Ninth Circuit Finds Article III Standing In Class Action Where The Only Harm Is The Act Of Unauthorized Disclosure Of Sensitive Information

By Gerald L. Maatman, Jamar Davis, and Caitlin Capriotti

Duane Morris Takeaways: On October 9, 2026, in Melissa Black and Miles Black v. IEC Group, Inc., No. 25-5952, 2026 U.S. App. LEXIS 30906 (9th Cir. Oct. 9, 2026), a panel for the Ninth Circuit, via an opinion written by Judge Eric. C. Tung, reversed the decision by the U.S. District Court for the District of Idaho dismissing a privacy class action for lack of subject matter jurisdiction for lack of injury. In the reversal, the Ninth Circuit held that the unauthorized disclosure of sensitive facts about Plaintiffs’ health that they entrusted Defendant to keep private is akin to a breach of confidence or contract. The act of disclosure, even without a formal privacy right, is an intangible harm sufficient for Article III standing. The case was remanded back to the District Court for further proceedings.

The decision is a must read for corporate counsel dealing with privacy class actions.

Case Background

Plaintiffs Miles and Melissa Black (“Plaintiffs”) receive health insurance from a plan administered by Defendant IEC Group, Inc. (“IEC”). Id. at *3. In August 2023, IEC sent Plaintiffs a letter informing them that some of their information was disclosed to unauthorized parties when an associate emailed a spreadsheet containing Plaintiffs’ sensitive health information to “on or more [plan] members.” Id. at *4. Information disclosed included: (1) first and last names, (2) unique tracking numbers, (3) provider names, (4) claim numbers, (5) dates of service, and (6) the amounts billed or paid. Id.

Plaintiffs brought a class action against IEC in the U.S. District Court for the District of Idaho claiming that when Plaintiffs entrusted their sensitive health information to IEC as a condition of their healthcare plan administration, IEC expressly and impliedly promised – through its Privacy Policy – to keep the information confidential and to not disclosure it to any third party without their consent, and to use reasonable methods to prevent such disclosure. Id. Plaintiffs allege that IEC breached those promises when they disclosed the confidential information without authorization, depriving Plaintiffs the benefit of their bargain and diminishing the value of the services rendered. Id.

The District Court granted IEC’s Rule 12(b)(1) motion to dismiss for lack of subject matter jurisdiction because it concluded that Plaintiffs did not suffer an injury in fact and thus did not have Article III standing. Id. at *5. The District Court held that to allege a concrete injury from disclosure of personal information, the Plaintiffs must show that the nature of the information disclosed, the context of the disclosure, and other alleged injuries associated with the disclosure demonstrate an imminent and substantial injury. Id.

The Ninth Circuit’s Analysis

The Ninth Circuit reversed. It began its ruling by reiterating the long-held standard that an “injury in fact” includes both tangible harms, such as physical harms or monetary loss, and traditionally recognized intangible harms, such as “reputational harms” or “harms specificized by the Constitution itself.” Id. at *6. The Ninth Circuit also opined that “Congress’s ‘judgement is also instructive and important,’ as that body is ‘well positioned to identify intangible harms that meet minimum Article III requirements.’” Id. at *7 (citing Spokeo, Inc. v. Robins, 578 U.S. 330, 341 (2016)).

In this case, the harm Plaintiffs alleged consisted of the unauthorized disclosure of sensitive facts about their health that they entrusted to IEC to keep private. Id. At this stage of litigation, there is no dispute that the disclosed information was sensitive to Plaintiffs nor that IEC promised Plaintiffs to keep this information private. Id. Thus, the harm that Plaintiffs allege from the disclosure resembled a breach of confidence and breach of contract, which courts have long held provides basis for a lawsuit. Id.

Under a breach of confidence claim, a defendant is liable for “the unconsented, unprivileged disclosure to a third party of nonpublic information that the defendant has learned within a confidential relationship. Id (citing Kamal v. J. Crew Grp., Inc., 918 F.3d 102, 114 (3d Cir. 2019)). The panel described cases going back to 1614 England to demonstrate this long held cause of action. See id *8-12. Ultimately, for a breach of confidence, “a trust betrayed is the harm.” Id. at *12 (emphasis in original). Further, the Ninth Circuit held that a privacy right is not necessary to find a breach of confidence claim. Id. at 13. A “breach of contract” claim only reinforces the breach of confidence standing. Id. at 15. Here, Plaintiffs have alleged a confidential relationship grounded in promises made by IEC, and a breach of those promises. Id.

Finally, the Ninth Circuit reasoned that Congress has confirmed that disclosure of private health information is a concrete injury through other legislation. Id. at 16. Congress passed the Health Insurance Portability and Accountability Act (HIPAA) and subsequent amendments to protect certain sensitive health information from improper disclosure. Id. While HIPAA does not provide a private cause of action, it does prohibit disclosure of private health information and even provides criminal liability for “knowingly ‘disclos[ing] individually identifiable health information to another person.’”Id (citing 42 U.S.C. § 1320d-6(a)(3)). Congress has made the determination that this information is sensitive enough to warrant statutory protection. Id. Thus, a disclosure of the private health information is a harm sufficient for Article III standing.

Implications for Companies

This case highlights the importance of maintaining confidentiality when handling sensitive personal information of their employees and customers. The Ninth Circuit has held that even if a private cause of action regarding privacy for a specific kind of sensitive information does not exist, unauthorized disclosure is itself harm in the context of Article III. Employers must ensure that their security protocols and storage of sensitive information passes muster in the digital age in order to avoid potential liability
Washington Supreme Court Rejects Privacy Class Action And Holds That Hospital’s Use Of Meta Pixel Does Not Violate State Privacy Act

By Gerald L. Maatman, Jr., Jennifer A. Riley, and Ryan T. Garippo

Duane Morris Takeaways:  On October 8, 2026, in Baker, et al. v. Seattle Children’s Hospital, No. 104590-5, 2026 WL 3023818 (Wash. Oct. 8, 2026), Justice Theodore J. Angelis of the Supreme Court of the State of Washington held that a hospital’s use of Meta Pixel’s advertising technology ( “Meta Pixel”) on its public website did not violate the Washington Privacy Act (“WPA”) because the plaintiffs’ website searches involved communications between a single individual and a website, and were not between “two or more individuals” as required by the WPA.  The decision is a significant win for companies that use website advertising technologies, like Meta Pixel, but its import may be limited to claims brought under Washington state law.

Case Background

Seattle Children’s Hospital (“SCH”) operates a public website that provides general information about the hospital, including a directory of health care professionals, hours of operation for clinics, and descriptions of health conditions.  The website also uses free software, called Meta Pixel, that allows websites to review visitors’ clicks, text searches, and page views.  Meta Pixel also allegedly relays content of such searches to Meta Platforms, Inc., which links that information to the Facebook or Instagram account of the website visitor for targeted advertising.

In 2023, Carly Baker, Amber Shavies, and Janssen Ramos Savoie (collectively, “Plaintiffs”) filed a putative class action against SCH.  Each of the Plaintiffs was a parent who alleged that they visited SCH’s public website to search for information regarding “their children’s medical conditions and for clinic operating hours, as well as visiting the patient portal, MyChart, to communicate with doctors and view their children’s electronic records and medical histories.”  Id. at *2.  SCH disputed that Meta Pixel was ever installed on the hospital’s MyChart patient portal and Plaintiffs “subsequently clarified that their claims targeted only the use of Pixel on SCH’s publicly available website.”  Id. at *2, n.5.

SCH moved to dismiss the complaint and argued, inter alia, that Plaintiffs’ searches and queries on the website were not “private communications” as defined by the WPA.  The trial court granted SCH’s motion to dismiss and dismissed the complaint with prejudice.  Plaintiffs appealed and the Washington Court of Appeals affirmed the dismissal on the ground that navigation of a website is not a “communication” as defined by the WPA.  See Baker v. Seattle Children’s Hosp., 35 Wash. App. 2d 1018 (2025).  Plaintiffs then petitioned the Washington Supreme Court for review and the petition was granted.

The Supreme Court’s Decision

In a unanimous result, Justice Angelis, writing for the majority of the Washington Supreme Court, affirmed the trial court’s dismissal but on a different basis than the Court of Appeals.

Instead of determining whether the Plaintiffs’ website activity constituted a “private communication,” the Supreme Court focused on a different part of the WPA’s text.  Justice Angelis explained that it is unlawful for “any individual, partnership, corporation, association, or the state of Washington” to intercept or record any “[p]rivate communication . . . between two or more individuals.”  RCW 9.73.030(1)(a).

Justice Angelis reasoned that, because only communications “between two or more individuals” are unlawful, SCH would need to be an “individual” for Plaintiffs’ theory to work.  Id.  But SCH is not an individual.  The WPA draws a distinction between “individuals” on the one hand and entities such as “partnership[s], corporation[s], association[s], or the state of Washington,” on the other.  Id.  Thus, because SCH is a corporation and “only one individual was involved in each communication, the [P]laintiffs do not have a claim under the WPA.”  Baker, 2026 WL 3023818, at *3.

Justice Angelis, however, took care to point out that it was immaterial that the WPA is “one of the most restrictive electronic surveillance laws ever promulgated” and that certain federal and California laws may prohibit such conduct.  Id. at *4 (quotations omitted).  He explained that those federal and state cases are “not instructive given the significant differences between the state and federal statutory schemes” and declined to consider such precedent.  Id. (quotations omitted).

Notably, Justice González and Justice Whitener wrote separately to concur in the result but express the view that “private communications transmitted between an individual and individuals working for a corporation are protected by” WPA.  Id. (González, J., concurring).  Instead, Justice González would have held that these communications were not between “two or more individuals” because the “parents’ private communications were directed at a server that returned stored content and not at another individual.”  Id. at *5 (González, J., concurring).  Thus, to Justice González, the material distinction was not a communication with a corporation but the nature of the underlying technology itself.

But nonetheless, the Washington Supreme Court unanimously affirmed the trial court’s dismissal with prejudice.

Implications For Companies

The Baker decision is a meaningful development for Washington companies that deploy advertising technologies, such as Meta Pixel, on their public-facing websites.  Although the unique language of the WPA likely makes this decision distinguishable from claims brought under the Electronic Communications Privacy Act or California Invasion of Privacy Act, this holding should knock out nearly all claims under the WPA as a matter of law.

Justice González’s concurrence, however, serves as a cautionary note.  Even though the majority opinion would seem to imply that you could never apply the WPA to communications with a corporation under any circumstances, there is at least a possibility that under different facts (e.g., such as communications directed to an individual staff member) the Washington Supreme Court would reach a different result.  Nonetheless, Baker is undoubtedly a tremendous win for Washington companies and corporate counsel should continue to monitor this blog to stay apprised of developments in class actions involving Meta Pixel litigation and digital privacy law.

California Federal Court Denies TikTok’s Motion To Dismiss Children’s Privacy Claims Based on Prior Class Action Settlements

By Gerald L. Maatman, Jr., Justin R. Donoho, and Hayley Ryan

Duane Morris Takeaways:  On September 23, 2026, in the case of In Re TikTok, Inc., Minor Privacy Litigation, No. MDL 25-3144, ECF No. 414 (C.D. Cal. Sept. 23, 2026), Judge George H. Wu of the U.S. District Court for the Central District of California issued a tentative ruling (adopted as final on September 24, 2026) denying TikTok’s motion to dismiss the Second Amended Consolidated Class Action Complaint in a multidistrict litigation brought by minors alleging that TikTok collected, shared, and exploited their personal information without parental consent in violation of the Children’s Online Privacy Protection Act (“COPPA”) and related state laws.

The ruling is significant because it rejected TikTok’s argument that two prior nationwide class action settlements – totaling over $93 million combined – barred the plaintiffs’ claims, holding that the record at the pleadings stage did not establish the named plaintiffs’ membership in those prior settlement classes.  For companies that have previously settled class actions, the decision underscores the risk that broad settlement releases may not foreclose subsequent litigation where class membership is not clearly established on the face of the pleadings.

Background

This case is one of a series of privacy class actions targeting TikTok and its parent companies, ByteDance Inc. and ByteDance Ltd.  The plaintiffs are minors who allege that while under the age of 13, their personal information was collected, shared, and exploited by TikTok without the parental notice and consent COPPA requires for children under 13. The plaintiffs seek to impose liability stretching back to March 28, 2019.

Two prior nationwide settlements form the backdrop of the dispute.  The first, T.K. v. Bytedance Technology Co., No. 1:19-CV-07915 (N.D. Ill.), followed the FTC’s 2019 enforcement action concerning COPPA violations by Musical.ly, TikTok’s predecessor, and settled for $1.1 million on behalf of approximately 6 million individuals who used Musical.ly or TikTok before August 22, 2022, while under the age of 13. The settlement included a broad release but no injunctive relief.  The second, In Re TikTok, Inc., Consumer Privacy Litigation, No. 1:20-CV-04699 (N.D. Ill.) (the “Privacy MDL”), consolidated lawsuits focused on TikTok’s use of algorithms, facial recognition, and other technologies to collect and transfer personally identifiable user data to servers in China, and settled for $92 million with broad injunctive relief.

In April 2025, the U.S. Judicial Panel on Multidistrict Litigation ordered the transfer of the present actions to the Central District of California.  After an initial partial dismissal of claims brought under laws of states without a domiciled plaintiff, the plaintiffs amended, and the defendants moved to dismiss the Second Amended Consolidated Class Action Complaint (“Complaint”), arguing that the T.K. and Privacy MDL settlements barred claims for conduct occurring before August 22, 2022, the cutoff date defining the later T.K. settlement class.  The dispositive question was therefore whether the pleadings themselves established that the named plaintiffs fell within those prior settlement classes.

The Court’s Decision

The Court denied TikTok’s motion to dismiss, finding that the defendants failed to establish, on the record available at the pleadings stage, that the named plaintiffs were members of the T.K. class. ECF No. 414 at 8-9.

At the heart of the ruling was a straightforward factual gap.  The T.K. settlement class included individuals who used TikTok or Musical.ly before August 22, 2022, while under the age of 13.  Id.  However, the Complaint did not allege the birth dates or first-use dates of any of the named plaintiffs – it alleged only that the plaintiffs were under 13 and used TikTok during the Class Period, defined as March 28, 2019, to the present.  Id. at 9.  The Court held that these allegations did not establish when within that period the plaintiffs used TikTok, and the judicially noticed materials likewise did not supply that information.  Id.

Even assuming none of the plaintiffs opted out of the prior settlements, the Court found that the defendants still had not shown the plaintiffs belonged to the prior classes in the first place.  Id.  As the Court stated, “[a] person need not opt out of a class to which that person never belonged.”  Id.

The Court also rejected TikTok’s argument that plaintiffs should not be allowed to avoid res judicata simply by “artfully pleading around” the relevant facts.  Id.  Because a plaintiff’s failure to anticipate and plead around an affirmative defense is not a pleading deficiency, as the Supreme Court explained in Jones v. Bock, 549 U.S. 199 (2007), the Court concluded that even plaintiffs who knew these defenses were coming, and knew their own ages and use histories, were not required to plead around TikTok’s affirmative defenses of release and preclusion, provided they otherwise sufficiently pleaded their causes of action. Id. at 10.

The Court further rejected TikTok’s alternative argument that, regardless of membership in the prior classes, plaintiffs either were precluded from, or lacked Article III standing to pursue, claims for the pre-August 2022 period.  Id.  TikTok reasoned that uncertainty about whether the named plaintiffs were under 13 and used TikTok before August 22, 2022, does not prevent dismissal because plaintiffs who meet those criteria are bound by the prior settlements, while plaintiffs who did not use TikTok during the relevant period cannot recover for that period and lack standing to represent those who did.  Id.  The Court disagreed.  The Court held that once a named plaintiff establishes individual standing, differences in injuries between the named plaintiffs and absent class members go to class certification rather than standing, the distinction drawn by the Ninth Circuit in Melendres v. Arpaio, 784 F.3d 1254 (9th Cir. 2015).  Id. at 11.  As the Court explained, “[w]hether Plaintiffs can represent class members who experienced that conduct earlier in the proposed Class Period concerns their representative capacity under Rule 23, and the possibility that Plaintiffs used TikTok only after August 22, 2022, does not defeat their standing to pursue the alleged claims.”  Id.  The Court likewise declined to redefine the class period at the pleading stage, holding that the issue is more appropriately addressed at class certification.  Id.

After oral argument on September 24, 2026, the Court adopted its tentative ruling as the final ruling.  See ECF No. 416.

Implications For Companies

This decision provides important guidance for any company facing follow-on privacy and/or adtech class action litigation after a prior settlement, by showing that broad settlement releases cannot be enforced at the motion-to-dismiss stage unless the defendant can demonstrate from the pleadings alone that the current plaintiffs were members of the prior class.  That is a high bar where the operative complaint does not specify individual plaintiffs’ ages or first-use dates, or other identifying information necessary to determine membership.

Of course, preclusion based on prior settlements is just one tool in a defendant’s kit for defeating class certification in privacy and adtech cases.  For example, in the related case of In Re TikTok, Inc., Consumer Privacy Litigation, 713 F. Supp. 3d 470 (N.D. Ill. 2024), the court declined to dismiss in-app browser claims on the basis of the prior $92 million settlement but left the door open to a different result upon further discovery.  Id. at 501-02.  There, the court observed that “the unusual and as-yet-undisclosed manner and method of the Original Plaintiffs’ post-settlement investigation leaves open the possibility that further information might alter this conclusion — for example, evidence that they recognized both the in-app browser’s risks and the potential to use them as the basis for a wiretapping theory of liability, but deliberately chose not to pursue this opportunity,” adding that “[s]uch evidence would be worth further attention, if not a different result.”  Id. at 501.  The court reinforced this point by noting that the original plaintiffs’ source code expert had been given “free rein to probe TikTok’s relevant technology” during confirmatory discovery.  Id. at 499.  Defendants facing successive adtech class actions should accordingly pursue targeted discovery into prior expert analyses and internal communications reflecting awareness of the privacy risks at issue — evidence that, under the court’s reasoning in In Re TikTok, Inc., Consumer Privacy Litigation, could compel preclusion of theories that were available but not pursued in the earlier proceeding.

California Federal Court Denies Class Certification In Adtech Case Due To Lack Of Article III Standing

By Gerald L. Maatman, Jr., Justin R. Donoho, and Hayley Ryan

Duane Morris Takeaways:  On September 21, 2026, in Smith, et al. v. Rack Room Shoes, Inc., No. 24-CV-6709 (N.D. Cal. Sept. 21, 2026), Judge Rita F. Lin of the U.S. District Court for the Northern District of California denied class certification in a case brought by consumers against an online shoe store company alleging that the company’s use of website advertising technology (“adtech”) violated the California Invasion of Privacy Act (“CIPA”) and Electronic Communications Privacy Act (“ECPA”).  The ruling is significant as it shows that before any class can be certified in the hundreds of adtech class actions filed in federal courts across the nation alleging that adtech violates privacy laws, plaintiffs not only bear the burden to establish, by the preponderance of the evidence, that they have suffered an Article III injury, but also cannot meet this burden by showing merely that they visited the defendant’s website at a time when adtech was installed on the website.

Background

This case is one of a legion of class actions that plaintiffs have filed nationwide alleging that third-party technology captured plaintiffs’ information and used it to facilitate targeted advertising. 

This software, often called advertising technologies or “adtech,” is a common feature of millions of consumer products and websites in operation today.  In adtech class actions, the key issue is often a claim brought under a the CIPA, the ECPA, or a variety of other statutes providing for statutory damages regardless of whether any actual injury occurred, because plaintiffs often seek millions (and sometimes even billions) of dollars, even from midsize companies, on the theory that hundreds of thousands of consumers or website visitors, times $5,000 per claimant in statutory damages under the CIPA and $10,000 per claimant in statutory damages under the ECPA, for example, equals a huge amount of damages.  Plaintiffs have filed the bulk of these types of lawsuits to date against healthcare providers, but they have filed suits against companies that span nearly every industry including retailers, consumer products, universities, and the adtech companies themselves.  Several of these cases have resulted in multimillion-dollar settlements, several have been dismissed, and the vast majority remain undecided. 

In Smith, the plaintiffs brought suit against Rack Room Shoes, Inc., an online shoe store company, alleging that in 2024, during their online web visits to purchase shoes from the company, the company had embedded on its website adtech supplied by Meta and other adtech companies that covertly intercepted the plaintiffs’ identities and interactions with the website, including the items the plaintiffs viewed, added to the their cart, and purchased, in alleged violation of the CIPA and the ECPA. 

The company answered the complaint, and the parties engaged in discovery, including the depositions of the plaintiffs and plaintiffs’ subpoenas to the adtech companies. 

Based on this discovery, the record reflected that in 2021 to 2023, the Meta pixel installed on the company’s website captured activities from devices and browsers that were signed into the plaintiffs’ accounts.  However, the plaintiffs provided no evidence that these 2021-2023 incidents involved their own web activities as opposed to activities of their family members using the same devices and browsers, that Meta captured any activity from the plaintiffs’ devices and browsers during their own sole 2024 visits, or that the other adtech installed on the company’s website captured any activities at all.

The plaintiffs moved for class certification, arguing that they had standing to bring their claims and that they satisfied Rule 23.

The Court’s Decision

The Court disagreed that the plaintiffs established standing and denied class certification on that basis without addressing or needing to address any of the parties’ arguments under Rule 23.

In their motion for class certification, the plaintiffs proffered two theories of injury in support of their argument that they had standing to bring their claims: one based on the actual interception of their information, and one based on the attempt to intercept their information.  (Slip Op. at 5.)

On the plaintiffs’ interception injury theory, the Court found no evidence that the Meta pixel embedded on the company’s website collected any data from the plaintiffs’ 2024 website visits, and no evidence that the activity that was recorded by Meta 2021-2023 was the plaintiffs’ own browsing activity.  Further, the Court rejected the plaintiffs’ argument that the company’s general use of the Meta pixel during 2024 was circumstantial evidence of actual tracking.  As the Court explained, citing the company’s expert testimony, the ability of adtech to collect and transmit data in a manner that can be linked to the website user “is impacted by many factors, including the browser being used, whether the browser and device are signed in to a social media account, and what cookie blocking features are enabled.”  (Id. at 7.)  In sum, the Court found that plaintiffs failed to present evidence from which a reasonable jury could find that any adtech installed on the company’s website collected any data attributable to the plaintiffs.

On the plaintiffs’ attempt injury theory, the Court found that the mere presence of active adtech on a company’s website does not bear the requisite close relationship to the type of harm traditionally at issue in intrusion upon seclusion and which type of harm the plaintiffs argued was the historical analog to the type of injury they suffered and thus sufficient to confer Article III standing.  On this point, the Court’s opinion turned on its finding that the plaintiffs presented no evidence that the adtech on the company’s website attempted to collect any “embarrassing, invasive, or otherwise private information.”  (Id. at 8.)  Further the Court found that the plaintiffs had no reasonable expectation of privacy in their web-browsing data due to the company’s privacy policy because the plaintiffs did not read it and the policy also did not create an expectation of privacy from adtech transmissions, and that even if plaintiffs had had a reasonable expectation of privacy, the plaintiffs failed to show that the mere presence of adtech was highly offensive.  (Id. at 9.)  In short, the Court held that “[t]he mere presence of active tracking software … on a website involving objectively non-sensitive information” does not bear a close relationship to the type of harm traditionally at issue in intrusion upon seclusion and, therefore, was insufficient to confer Article III standing.

Implications For Companies

Smith provides powerful precedent for any company opposing adtech class action claims where plaintiffs lack evidence from which a reasonable jury could find that any adtech installed on the company’s website actually collected any data attributable to the plaintiffs, by showing that any number of issues could have prevented such collection, such as the browser being used, whether the browser and device are signed in to a social media account, and what cookie blocking features are enabled.

Of course, Smith is just one tool in a defendant’s kit for defeating class certification in adtech cases.  Another is that even when named plaintiffs can establish that adtech collected data attributable to themselves (unlike in Smith), the same factors identified in Smith — browser type, social media account login status, cookie blocking features — are individualized issues that prevent named plaintiffs from establishing the defendant’s liability to alleged class members under Rule 23, as we blogged about here.

Seventh Circuit Undoes Novel Privacy Class Settlement Due To Lack Of Separate Representatives For Nationwide Class And State Sub-Classes

By Gerald L. Maatman, Jr., Hayley Ryan, and Tyler Zmick

Duane Morris Takeaways:  On July 13, 2026, in the case captioned as In Re Clearview AI, Inc. Consumer Privacy Litigation, No. 25-1673, 2026 U.S. App. LEXIS 20406 (7th Cir. July 13, 2026), the U.S. Court of Appeals for the Seventh Circuit vacated a district court’s approval of a novel class action settlement between Clearview and individuals alleging that Clearview violated privacy laws by “scraping” their public photos from the internet to improve the company’s facial recognition technology. The Seventh Circuit held that the absence of separate class representatives for the nationwide class and the state-specific subclasses was a “key procedural problem” requiring vacatur of the settlement.

This decision is an important reminder that courts evaluating class settlements will closely scrutinize whether all classes and subclasses have adequate structural protections, including separate class representatives with separate counsel in cases where class members may have divergent interests.

Background

Clearview operates “a search engine for faces,” whereby the company scrapes photographs of individuals from public websites and analyzes them using artificial intelligence to generate “facial vectors” reflecting the geometry of a person’s facial features. Id. at *3. A search of Clearview’s database using a photograph of a person returns other photographs of that same person, together with links to the websites where the photographs were located.

The case arose from 11 putative class actions filed in federal district courts against Clearview and related defendants, which were ultimately transferred to the Northern District of Illinois for coordinated pretrial proceedings. 

After the appointment of interim lead class counsel, Plaintiffs filed a consolidated complaint asserting claims for declaratory judgment and unjust enrichment on behalf of a Nationwide Class comprised of all individuals in the United States whose biometric data was or is contained in Clearview’s database. Plaintiffs also asserted claims under the Illinois Biometric Information Privacy Act (“BIPA”) on behalf of an Illinois Subclass; claims under various California laws on behalf of a California Subclass; claims under New York’s civil rights code on behalf of a New York Subclass; and claims under the Virginia Computer Crimes Act and for statutory commercial misappropriation of identity on behalf of a Virginia Sub-class.

The parties first engaged in settlement discussions in 2022, which failed because Clearview lacked the financial ability to make the substantial immediate payments sought by Plaintiffs. But after mediating the case in 2023, the parties agreed to a settlement structure under which class members would acquire equity stake in Clearview. Specifically, the settlement provided that upon an initial public offering or a merger, consolidation, or sale of Clearview, the Class would receive a payment equivalent to a 23% equity stake in Clearview as of September 6, 2023. Alternatively, in lieu of that payment, the court-appointed settlement master could either (i) sell the settlement stake to a third party for a “commercially reasonable price” or (ii) make a cash demand equal to 17% of Clearview’s revenue from the date of final approval of the settlement until the date of such demand. Id. at *7.

The settlement stake itself would be divided unevenly among Class members based on the specific forms of relief available under the relevant state laws: ten shares to each member of the Illinois Subclass; five shares to each member of the California, New York, and Virginia Subclasses; and just one share to each member of the Nationwide Class. Notably, none of the eight original class representatives agreed to the settlement, so lead class counsel replaced them with four new representatives, each of whom belonged to one of the “favored” state-specific sub-classes.

After the District Court granted final approval, Objectors Robert Weissman and Rick Claypool, both members of the Nationwide Class, appealed. They argued that the settlement was not “fair, reasonable, and adequate” because (i) it did not provide injunctive relief, (ii) the future equity-stake and cash-demand fallback made the settlement’s value too uncertain, and (iii) the Nationwide Class lacked separate representation during the settlement negotiations.

The Seventh Circuit’s Decision

The Seventh Circuit vacated the District Court’s approval of the settlement and remanded the case for further proceedings. 

The Seventh Circuit rejected the Objectors’ two substantive challenges to the settlement, concluding that a fair settlement did not necessarily require injunctive relief and that the uncertainty associated with the equity-based structure was not disqualifying because “uncertainty is inherent” in such settlements. Id. at *11, 16.

The Seventh Circuit, however, agreed with the Objectors’ third argument regarding the settlement being deficient due to the absence of a separate Nationwide class representative with separate counsel. The Seventh Circuit explained that class action litigation relies on “structural assurance of fair and adequate representation for the diverse groups and individuals affected.” Id. at *23 (quoting Amchem Products, Inc. v. Windsor, 521 U.S. 591, 627 (1997)). One such “important structural feature” is the requirement that class representatives, who owe a fiduciary duty to absent class members, approve any proposed settlement. Id.

The Seventh Circuit emphasized that “[n]ot just any representative will do” and that the critical question is whether “the court can be confident that absent class members have been represented fairly.” Id. at *24-25. The Seventh Circuit concluded that the Nationwide Class lacked adequate representation because “none of the named class representatives was in a position to represent solely the interests of the Nationwide Class in allocating the settlement.” Id. at *29; see id. at *31 (“Appointment of separately counseled class representatives for identifiable, significantly different groups of claimants with fundamentally conflicting interests is Rule 23’s primary mechanism for such protection.”).

On this basis, the Seventh Circuit vacated the District Court’s approval of the settlement and remanded the case.

Implications For Companies

The Seventh Circuit’s decision in In Re Clearview AI, Inc. Consumer Privacy Litigation is a cautionary tale for companies structuring, or defending, class action settlements involving multiple classes or subclasses with potentially divergent interests. Where claimants fall into distinct groups with conflicting stakes in how settlement proceeds are allocated, courts will expect each group to have its own class representative with its own counsel at the negotiating table. A settlement that may be fair and reasonable on its face can be vacated if it lacks these structural safeguards, as without such protections a reviewing court cannot confirm that each class’s interests was independently considered during negotiations. Companies should keep this principle in mind at the outset of class settlement negotiations to avoid the possibility of a proposed class settlement failing on appeal due to the lack of necessary structural safeguards.

Third Circuit Holds That Unauthorized Collection Of Credit Card Information Via Session Replay Code Confers Article III Standing, Creating Split Of Authority

By Gerald L. Maatman, Jr., Justin Donoho, and Hayley Ryan

Duane Morris Takeaways: On May 11, 2026, in In Re BPS Direct, LLC; Cabela’s, LLC Wiretapping Litigation, No. 23-3235, 2026 WL 1280969 (3d Cir. May 11, 2026), the U.S. Court of Appeals for the Third Circuit reversed a federal district court’s dismissal of a class action alleging that defendants’ use of session replay code, a form of website analytics technology, violated federal and state privacy laws. The Third Circuit held that two plaintiffs who made purchases on the defendants’ websites had standing to sue because the session replay code collected their credit card information without consent, an alleged injury the Third Circuit deemed analogous to the common law tort intrusion upon seclusion. Id. at *6-7.

This ruling is significant in that it shows that in class actions seeking millions (or billions) in dollars in statutory damages under federal and state data privacy laws for alleged use of session replay code, the Third Circuit has distinguished itself from California District Courts, which have held that there is no reasonable expectation of privacy in credit card information collected by session replay code.  Companies operating in the Third Circuit should take note as the legal risk of session replay code has meaningfully shifted in that jurisdiction. 

Background

Many companies embed their websites with session replay code and other similar software such as Google Analytics and the Meta Pixel in order to perform website analytics and/or targeted advertising. All of these various technologies capture users’ browsing behaviors and cryptographically transmit this data to algorithms residing on the software providers’ servers.  Upon entry into the algorithm, this data is typically anonymized, aggregated, and not alleged to have been viewed or accessible by any human.  In addition, session replay code (unlike other website analytics and advertising technologies) is typically alleged to record and store “videos” of “all mouse movements, clicks, scrolls, zooms, window resizes, keystrokes, [and] text entries,” so that the session replay provider can provide that information back to the company “in a format that [the company] can use for its business purposes.” Id. at *1, 5. Plaintiffs across the country have filed multitudes of class actions challenging these various website analytics and advertising practices under federal and state privacy laws, targeting companies in virtually every industry, including healthcare, retail, education, and consumer products.  Some cases have resulted in multimillion-dollar settlements, others have been dismissed, and the vast majority remain undecided.  In these session replay and other data privacy class actions, the central question is often whether the specific data captured is sufficiently sensitive or personally identifying to establish a cognizable legal injury.

In In re BPS Direct, LLC, eight named plaintiffs sued the defendant retailers, alleging that session replay code embedded on their websites captured users’ interactions, including “mouse clicks and movements, keystrokes, search terms, substantive information inputted …, pages and content viewed …, scroll movement[s], and copy and paste actions.” Id. at *2.  Plaintiffs asserted claims under the federal Wiretap Act, 18 U.S.C. § 2510 et seq., and the Computer Fraud and Abuse Act, 18 U.S.C. § 1030 et seq., along with several state and common law causes of action. Id.

The plaintiffs fell into two groups. Two plaintiffs made purchases on the defendants’ websites and entered his or her “name, address, and payment and billing information” into text fields. Id. The remaining six plaintiffs browsed the websites without making purchases and did not enter any personally identifying information while browsing the websites.  Id.

Defendants moved to dismiss for lack of Article III standing under Federal Rule of Civil Procedure 12(b)(1) and for failure to state a claim under Federal Rule of Civil Procedure 12(b)(6).  The District Court granted the motion, dismissing the non-purchasing plaintiffs’ claims with prejudice, finding that, after two attempts, they could not establish concrete harm “because they did not make purchases on the Websites or engage in any activity prompting their browsers to send highly sensitive personal information such as medical diagnosis information or financial data from banks or credit cards.” 705 F. Supp. 3d 333, 367 (E.D. Pa. 2023).  The claims of the two purchasing plaintiffs were dismissed without prejudice. Id. Rather than amend, those two plaintiffs filed a notice of intent to stand on their allegations, and all eight plaintiffs appealed.  2026 WL 1280969, at *2-3.

The Third Circuit’s Decision

The Third Circuit reversed the dismissal of the purchasing plaintiffs’ claims and modified the dismissal of the non-purchasing plaintiffs’ claims from with prejudice to without prejudice.  Id. at *1. 

The Third Circuit analyzed standing under two analogous common law torts: (1) public disclosure of private facts, and (2) intrusion upon seclusion. It held that none of the plaintiffs had standing under the first theory.  As to the non-purchasing plaintiffs, their browsing data was neither sensitive nor personally identifiable. As to the purchasing plaintiffs, their information was not publicly disclosed.  Id. at *4-5.

The Third Circuit held that only the two purchasing plaintiffs had standing under the intrusion upon seclusion theory. Id. at *3.  Under that common law tort, “[o]ne who intentionally intrudes, physically or otherwise, upon the solitude or seclusion of another or his private affairs or concerns, is subject to liability to the other for invasion of his privacy, if the intrusion would be highly offensive to a reasonable person.” Id. at *5 (citing Restatement (Second) of Torts § 652B (1977)). The Third Circuit concluded that the two purchasing plaintiffs had entered “personal or sensitive” information – specifically their “complete credit card or debit card numbers” – when making purchases on the defendants’ websites. Id. at *7. The Third Circuit reasoned that “[j]ust as media consumption is sensitive and historically private, so is a person’s complete credit card or debit card number.” Id.

Accordingly, the Third Circuit held that these two plaintiffs had standing based on their allegations that defendants embedded session replay code in their websites, allowing third-party adtech providers to “surreptitiously record their billing and payment information absent consent.” Id.

Implications For Companies

This ruling puts the Third Circuit at odds with California District Courts, which have reached the opposite conclusion in two session replay cases. See Thomas v. Papa Johns Int’l, Inc., 2024 WL 2060140, at *5 (S.D. Cal. May 8, 2024) (plaintiff’s “name, address, credit card number(s), and billing information” collected via session replay is “not information over which society is prepared to recognize a reasonable expectation of privacy”); Saleh v. Nike, Inc., 562 F. Supp. 3d 503, 525 (C.D. Cal. 2021) (collection via session replay of a website user’s “payment card information, including card number, expiration date, and CCV code” without consent was insufficient to constitute an invasion of privacy).

In the Third Circuit, session replay is no longer just an analytics tool – it carries significant legal risk for website operators.  Companies facing session replay class actions in the Third Circuit should shift their litigation strategy accordingly and consider moving beyond standing arguments, including demonstrating that plaintiffs cannot meet their burden of proof on the elements of the claims asserted.

Given the volume of session replay and similar litigation pending nationwide and the significant statutory damages at stake, this decision warrants close attention from any company whose website uses session replay code or similar technologies.

Wisconsin Federal Court Remands Privacy Class Action Lawsuit Based On Lack Of No Injury From Google Analytics Data Tracking

By Gerald L. Maatman, Jr., Bernadette M. Coyle, and Andrew P. Quay

Duane Morris Takeaways: On May 1, 2026, in Brahm, et al. v. Hospital Sisters Health System, et al., No. 23-CV-444, 2026 U.S. Dist. LEXIS 96866 (W.D. Wis. May 1, 2026), Judge William M. Conley of the U.S. District Court for the Western District of Wisconsin remanded a putative class action to state court after finding that Plaintiffs lacked Article III standing to pursue claims that healthcare defendants’ use of Google Analytics on patient portals resulted in unauthorized disclosure of protected health information (“PHI”) to Google.  Id. at *2-3.  The Court held that Plaintiffs’ lack of evidence of actual harm, together with their theory of future harm, was insufficient to confer standing.  Id. at *3.  The decision reinforces the growing trend among federal courts requiring proof that disclosed data was actually used to identify individuals, not merely that such identification was theoretically possible.

Case Background

The Defendant healthcare companies operate public websites and authenticated MyChart patient portals as “MyHSHS” and “MyPrevea,” which allow patients to log in with a username and password to access their medical records, schedule appointments, and pay bills.  Id. at *4.  Between at least 2016 and 2023, Defendants deployed Google Analytics tracking technology on their public websites, within patient portals on their websites, and on MyPrevea’s login page and app.  Id. at *6.  Whenever a user visits Defendants’ websites or portals, Google Analytics gathers information about the user’s interactions and shares certain transmissions with Google.  Id. at *7.

Plaintiffs asserted that Google Analytics routinely disclosed patients’ identities and protected health care information to third-party websites like Google without the patients’ knowledge or consent.  Id. at *1.  Plaintiffs alleged that they began seeing Facebook advertisements related to their specific medical conditions after visiting Defendants’ portals or websites.  Id. at *5.  However, Plaintiffs also searched about their medical conditions or treatment online and have had their personal information involuntarily exposed to third parties by entities unrelated to the litigation.  Id.  None of the Plaintiffs had ever tried or intended to sell their PHI, nor did they claim to have suffered any out-of-pocket expenses as a result of Defendants’ allegedly wrongful disclosures.  Id. at *10.  Nonetheless, they sought actual damages based on the alleged “diminished sales value of their PHI,” as well as statutory and nominal damages.  Id.

Plaintiffs alleged claims for violation of federal and state wiretapping statutes, as well as Wisconsin common and statutory laws for breach of duty of confidentiality, breach of implied contract to protect privacy, public disclosure of private facts, and unjust enrichment.  Id. at *3.  Plaintiffs moved to certify four subclasses, while Defendants moved for summary judgment as to all claims.  Id.  

The Court’s Opinion

The Court addressed the “threshold question” of Article III standing on its own initiative, noting that Defendants’ summary judgment motion called Plaintiffs’ standing into question and standing “is jurisdictional and cannot be waived” and must be “secured at each stage of the litigation.”  Id. at *12.  While the Court had previously allowed the original named Plaintiff to proceed past the motion to dismiss stage because it found her allegations of injury sufficient at the pleading stage, the Court explained that with a full record at the summary judgment stage, Plaintiffs failed to present sufficient evidence of a concrete injury-in-fact on multiple grounds.  Id. 

First, as to Plaintiffs’ tort claims for invasion of privacy and breach of fiduciary duty, the Court found no evidence from which a reasonable jury could conclude that their patient identity or PHI was actually disclosed to Google, disclosed by Google, or used by Google inappropriately.  Id. at *17.  Plaintiffs’ evidence did not establish that any of the disclosed anonymous information was actually used by Google or another third party to identify them.  Id.  

Despite Plaintiffs’ expert opining that Google’s systems had the “technical capability and documented practice” of linking information to specific individuals, the Court determined that the capabilities of Google’s systems were insufficient to demonstrate what it actually did.  Id. at *19.  Further, Plaintiffs failed to proffer evidence showing that Defendants caused Plaintiffs’ PHI to be shared, as opposed to other third parties or Plaintiffs themselves through their own voluntary internet disclosures.  Id. at *20. 

Relying on the Seventh Circuit’s decision in Dinerstein v. Google, LLC, 73 F.4th 502 (7th Cir. 2023), the Court emphasized that Plaintiffs “must still present sufficient evidence that Google Analytics actually worked as allegedly intended, which they have failed to do in this case,” and therefore, Plaintiffs failed to show a concrete injury to support standing under Article III.  2026 U.S. Dist. LEXIS 96866, at *23.  The risk of Google or other third parties identifying Plaintiffs at a later date by leveraging the data obtained from Defendants was “not sufficiently imminent to obtain relief in federal court.”  Id.

Second, as to the breach of implied contract claim, the Court found that Plaintiffs lacked standing because their asserted pecuniary harm based on the diminished sales value of their PHI or nominal damages, without any actual harm, was an injury in law and not an injury-in-fact as required by Article III.  Id. at *24-25.

Third, Plaintiffs alternatively asserted unjust enrichment, arguing that Defendants retained without compensation Plaintiffs’ PHI and then disclosed this information to third parties for Defendants’ own gain.  Id. at *26.  However, the Court found that without any evidence of improper disclosure, Plaintiffs’ alleged pecuniary injury was “simply speculative and insufficient to confer standing.”  Id. at *27.

Fourth, the wiretapping claims likewise failed.  Although Plaintiffs sought statutory damages, the Court held that a statutory violation on its own does not confer standing without an underlying concrete, particularized injury.  Id. at *28 (citing TransUnion LLC v. Ramirez, 594 U.S. 413, 427 (2021)).

Having found that Plaintiffs lacked standing as to all claims, the Court remanded the case to Wisconsin state court for further proceedings.  Id.

Implications For Companies

Brahm reinforces that plaintiffs challenging tracking technology must present actual evidence identifying what allegedly private information was disclosed and cannot rely on abstract and speculative alleged injuries to confer Article III standing.  Asserting an Article III standing defense remains an effective defense that companies should consider throughout litigation, balanced against the prospect of the case continuing in state court.

Data Security and Privacy Liability – Takeaways From The Sedona Conference Working Group 11 Annual Meeting in Kansas City, MO

By Justin R. Donoho

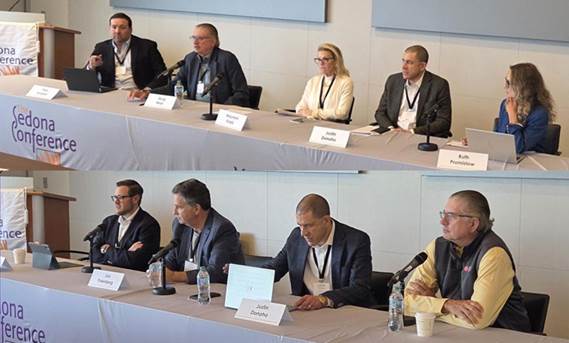
Duane Morris Takeaways: Data privacy and data breach class action litigation continue to explode.  At the Sedona Conference Working Group 11 on Data Security and Privacy Liability, in Kansas City, Missouri, on May 5-6, 2025, Justin Donoho of the Duane Morris Class Action Defense Group served as a dialogue leader for two panel discussions, “Privacy and Data Security Litigation Update” and “Legislative Drafting Considerations: Lessons from Colorado’s Privacy and AI Law Intersection.”  The working group meeting, which spanned two days and had over 50 participants, produced excellent dialogues on these topics and others including unique procedural aspects of data breach class actions, data privacy primer, onward transfer of consumer PII in M&A and bankruptcy contexts, privacy and data security state regulator roundtable, and application of attorney-client privilege in the cybersecurity context.

The Conference’s robust agenda featured over 30 dialogue leaders from a wide array of backgrounds, including federal and state regulators and governmental officials, data security industry experts, in-house attorneys, cyberlaw professors, plaintiffs’ attorneys, and defense attorneys.  In a masterful way, the agenda provided valuable insights for participants toward this working group’s mission, which is to identify and comment on trends in data security and privacy law, in an effort to help organizations prepare for and respond to data breaches, and to assist attorneys and judicial officers in resolving questions of legal liability and damages.

Justin had the privilege of speaking about current trends in data privacy class actions and lessons from the intersection of the Colorado Privacy Act (CPA) and Colorado AI Act (CAIA) and how these lessons might guide future legislatures when drafting AI and data privacy statutes.  Highlights from his presentations included two recent cases resulting in helpful precedent for defendants facing cases alleging privacy violations for their uses of website advertising technologies (adtech), including a case that disposed of a claim under the California Invasion of Privacy Act under the rule of lenity (see here), and a case that dismissed an adtech class action due to failure to allege highly offensive conduct (see here).

Finally, one of the greatest joys of participating in Sedona Conference meetings is the opportunity to draw on the wisdom of fellow presenters and other participants from around the globe.  Highlights included:

  1. Litigators from both sides of the “v.” and a neutral debating early case procedural rules and practices, choice of law, and discovery mechanisms in the context of data breach class actions, with an unprompted shoutout to the Duane Morris Class Action Review for supplying statistics.
  2. Sedona Conference veterans discussing Sedona’s latest version of a data privacy primer and the proper level of detail to include in this document ten years in the making in order to keep it reasonably current to account for the rapid evolution of data privacy laws and related developments in artificial intelligence.
  3. Panelists with different backgrounds discussing the law regarding when a company that has obtained personal data with consent can and cannot transfer the data in M&A and bankruptcy contexts.
  4. A lively dialogue among some of my panelists and other participants regarding trends in decisions regarding mass arbitration protocols and whether a company’s use of website advertising technology is highly offensive to a reasonable person.
  5. Federal and state regulators discussing enforcement priorities and issuances of advisory opinions in the contexts of data breaches, alleged data privacy violations, and concerns regarding national security.
  6. Data breach litigators discussing factors to consider when conducting dual track investigations following a cybersecurity incident in order to segregate and maintain confidentiality over attorney work product and attorney-client communications.
  7. A lively dialogue among some of my panelists and other participants regarding whether compliance with AI and antidiscrimination statutes should provide a safe harbor for compliance with data privacy statutes including, for example, the heavily litigated California Invasion of Privacy Act.

Thank you to the Sedona Conference Working Group 11 and its incredible team, the fellow dialogue leaders, the engaging participants, and all others who helped make this meeting in Redmond, Washington, an informative and unforgettable experience.

Finally, I want to thank to share the exciting news that I have been selected as a new steering committee member of Working Group 11.  Thank you Sedona!  In this role, I will help lead the identification of cutting-edge issues and oversee development of principles, guidelines, commentaries and other projects representing the work product of the Sedona Conference.

For more information on the Duane Morris Class Action Group, including its Data Privacy Class Action Review e-book, and Data Breach Class Action Review e-book, please click the links here and here.

AbbVie Defeats Genetic Privacy Class Action Because Request For Plaintiff’s Family Medical History Was Not A “Condition Of Employment”

By Gerald L. Maatman, Jr., Tyler Zmick, and Hayley Ryan

Duane Morris Takeaways:  In Henry v. AbbVie, Inc., No. 23-CV-16830 (N.D. Ill. Mar. 20, 2026), Judge Manish S. Shah of the U.S. District Court for the Northern District of Illinois granted defendant’s motion for summary judgment and dismissed a claim brought under the Illinois Genetic Information Privacy Act (“GIPA”). In his ruling, Judge Shah determined that the alleged request for plaintiff’s family medical history (which history Plaintiff did not provide) during his pre-employment medical screening was not a “condition of employment.” The decision is welcome news for employers that ask employees to undergo medical exams. The ruling indicates that an employer does not necessarily request genetic information “as a condition of employment” by requiring an employee to undergo a medical exam (even if an employee is asked to disclose genetic information during the exam).

Background

Plaintiff Daniel Henry was assigned to work for Defendant AbbVie, Inc., a biopharmaceutical company. During the onboarding process, Plaintiff was required to undergo a “medical surveillance,” which included “questionnaires, blood work, and a brief physical exam.” Henry v. AbbVie, Inc., 2026 WL 788630, at *2 (N.D. Ill. Mar. 20, 2026).

AbbVie used Premise Health, a third-party healthcare provider, to conduct Plaintiff’s medical screening. During the screening, Premise Health nurses asked Plaintiff to complete a written questionnaire and to undergo a physical examination. “Section U” of the questionnaire asked for Plaintiff’s genetic information (specifically, his family medical history), though Plaintiff did not complete that part of the form. Plaintiff claimed that nurses also verbally asked for his family medical history during the physical exam. After the exam, Plaintiff worked at an AbbVie facility in Illinois for four months.

Plaintiff subsequently sued AbbVie under the GIPA, alleging that the company violated Section 25(c)(1) of the statute by “solicit[ing], request[ing], [or] requir[ing] . . . genetic information of a person or a family member of the person . . . as a condition of employment [or] preemployment application.”  410 ILCS 513/25(c)(1).

AbbVie first responded to Plaintiff’s Complaint by moving to dismiss under Federal Rule of Civil Procedure 12(b)(6). Judge Shah denied AbbVie’s motion to dismiss after determining that the family medical history information sought during the medical screening constituted “genetic information” under the GIPA. See Henry v. AbbVie, Inc., 2024 WL 4278070, at *5-6 (N.D. Ill. Sept. 24, 2024).

AbbVie later moved for summary judgment, arguing that: (1) AbbVie did not request Plaintiff’s genetic information because third-party Premise Health (not AbbVie) conducted the screening; (2) even if AbbVie requested Plaintiff’s genetic information, the request was inadvertent because the medical questionnaire instructed Plaintiff to not disclose genetic information; and (3) AbbVie did not condition Plaintiff’s work status or assignment on any request for his genetic information.

The Court’s Decision

The Court granted AbbVie’s motion for summary judgment. While the Court was not persuaded by AbbVie’s first two arguments, it concluded that AbbVie’s third argument warranted dismissal of Plaintiff’s GIPA claim.

Request for Genetic Information

The Court first considered whether AbbVie can be characterized as having requested Plaintiff’s family medical history despite third-party Premise Health having conducted the medical screening. In answering in the affirmative, the Court relied on the GIPA’s incorporation of certain protections found in the federal Genetic Information Nondiscrimination Act (“GINA”). See 410 ILCS 513/25(a) (“An employer … shall treat genetic testing and genetic information in such a manner that is consistent with the requirements of federal law, including but not limited to [GINA].”). The Court cited a regulation promulgated under GINA providing that an employer that requires employees or applicants to undergo medical examinations “must tell health care providers not to collect genetic information, including family medical history, as part of a medical examination intended to determine the ability to perform a job.” 29 C.F.R. § 1635.8(d). Based on this federal regulation, the Court concluded that AbbVie “[n]ot telling Premise Health to elicit genetic information is not enough; the [GIPA] requires an affirmative instruction not to elicit it.” Henry, 2026 WL 788630, at *5.

Inadvertent Disclosure

AbbVie’s second argument turned on the GIPA’s “inadvertent exception,” which states that “inadvertently requesting family medical history by an employer … does not violate this Act.” 410 ILCS 513/25(g). The Court observed that AbbVie’s health questionnaire advised Plaintiff to “not provide any genetic information, including family medical history.” Henry, 2026 WL 788630, at *6 (citation omitted). Thus, the Court held that the inadvertent exception barred Plaintiff’s claim to the extent it was premised on the written questionnaire. See id. (“The disclaimer on AbbVie’s form was enough to make any disclosure on the form inadvertent.”). But the Court determined that the exception did not necessarily bar Plaintiff’s claim to the extent it was premised on nurses orally asking for his family medical history. See id. (“[T]he written disclaimer in the form does not necessarily mean that [Plaintiff] knew that he should not disclose genetic information in response to verbal questions during his physical exam.”) (emphasis added).

Request as a Condition of Employment

Finally, the Court turned to AbbVie’s argument that Plaintiff’s claim failed because any request for his family medical history was not a condition of his employment. See 410 ILCS 513/25(c)(1) (an employer may not “solicit, request, [or] require … genetic information of a person or a family member of the person … as a condition of employment [or] preemployment application”) (emphasis added). The Court agreed with AbbVie and granted the company’s motion for summary judgment on this basis, holding that no genuine issue of material fact existed regarding AbbVie’s request for Plaintiff’s family medical history not having been a condition of his employment. The Court further noted that “the request for genetic information on the written questionnaire was not a condition of [Plaintiff’s] employment, for the simple fact that [Plaintiff] did not fill out that section and it did not affect his employment with AbbVie.” Henry, 2026 WL 788630, at *6.

Moreover, the Court concluded that even if Plaintiff was required to undergo a medical exam to be eligible to work at AbbVie, that did not mean that the verbal request for his family medical history (made during the exam) was a condition of his employment. See id. at *7. The Court thus recognized an important distinction between (i) AbbVie requiring Plaintiff to undergo a medical screening as a condition of employment and (ii) AbbVie specifically requesting Plaintiff’s family medical history as a condition of employment. See id. (“[T]hat [Plaintiff] could not decline to complete his medical surveillance does not create a genuine dispute over whether the verbal request during his exam was a condition of his employment. The undisputed evidence is that a contractor could decline parts of the surveillance and still have the surveillance considered completed.”). Accordingly, because AbbVie did not condition Plaintiff’s employment on a request for his genetic information, the Court granted summary judgment in the company’s favor.

Takeaways For Companies

As noted in a prior blog post, recent decisions suggest that courts may be hesitant to dismiss GIPA claims (especially at the pleading stage). Given the GIPA statute’s strict penalty provision – under which statutory damages can quickly become significant ($2,500 per negligent violation and $15,000 per intentional or reckless violation, see 410 ILCS 513/40(a)(1)-(2)) – we have advised employers to ensure they comply with the statute regarding any health screenings they ask applicants or employees to complete (including by explicitly advising applicants and employees not to disclose their family medical histories during the screenings).

In this plaintiff-friendly litigation landscape, the Henry decision comes as welcome news for GIPA defendants and companies that have employees undergo medical screenings. Importantly, Henry suggests that an employer does not necessarily violate the GIPA by requesting an employee’s genetic information “as a condition of employment” by merely directing her to undergo a medical exam (during which the employee may or may not be asked to provide her family medical history).

Massachusetts Federal Court Dismisses Adtech ECPA Class Action For Failure To Allege Defendants Purposefully Committed A Criminal Act, Furthering Split Of Authority

By Gerald L. Maatman, Jr., Justin Donoho, and Hayley Ryan

Duane Morris Takeaways: On March 6, 2026, in Progin v. UMass Memorial Health Care, Inc., No. 25-CV-40003, 2026 U.S. Dist. LEXIS 46522 (D. Mass. Mar. 6, 2026), Judge Allison D. Burroughs of the U.S. District Court for the District of Massachusetts granted a motion to dismiss a class action complaint brought by website users against Massachusetts health care and hospital entities. Plaintiffs alleged that the defendants’ use of website advertising technology (“adtech”) violated the federal Wiretap Act, also known as the Electronic Communications Privacy Act (“ECPA”).  Following another similar ruling in the same court,  see Goulart v. Cape Cod Healthcare, Inc., 2025 U.S. Dist. LEXIS 119435 (D. Mass. June 24, 2025),  the decision is significant because it reflects the Massachusetts Federal court’s alignment with other federal courts (including the U.S. District Court for the Southern District of Texas, as we blogged about here) that have interpreted the ECPA in a defense-friendly manner. In contrast, courts in other jurisdictions (including Illinois Federal courts, as we blogged about here) have adopted more plaintiff-friendly interpretations, further deepening the emerging split of authority in adtech privacy litigation.

Background

Progin is one of a legion of class actions that plaintiffs have filed nationwide alleging that Meta Pixel, Google Analytics, and other similar software embedded in websites secretly captured plaintiffs’ web-browsing data and transmitted that data to Meta, Google, and other online advertising agencies and data analytics companies.

In these adtech and similar internet-based technology class actions, plaintiffs frequently rely on the ECPA’s statutory damages provision. Their theory is simple: multiply the number of website visitors – potentially hundreds of thousands – by $10,000 in statutory damages per claimant to produce enormous potential exposure. Although plaintiffs have filed a majority of these lawsuits to date against healthcare providers, they have filed suits against companies that span nearly every industry including education, retailers, and consumer products. Some of these cases have resulted in multimillion-dollar settlements, while others have been dismissed at the pleading stage (as we blogged about here) or the summary judgment stage (as we blogged about here), and the vast majority remain undecided.

In Progin, the plaintiffs sued a group of health care and hospital entities, seeking to represent a class of patients whose personal health information was allegedly disclosed by the Meta Pixel installed on defendants’ websites. The plaintiffs claimed that these alleged transmissions constituted an “interception” by defendants in violation of the ECPA.

Under the ECPA, a “party to the communication” generally cannot be sued unless it intercepted the communication “for the purpose of committing any criminal or tortious act.” 18 U.S.C. § 2511(2)(d). This provision is commonly referred to as the “crime-tort exception.”

Plaintiffs argued that alleged violations of the Health Insurance Portability and Accountability Act (HIPAA) served as the predicate crime to trigger this exception. Specifically, plaintiffs argued that defendants were liable under the crime-tort exception because they intercepted and disclosed plaintiffs’ communications and personal information to third parties without consent in violation of HIPAA. 2026 U.S. Dist. LEXIS 46522, at *11.

The defendants moved to dismiss, arguing that the crime-tort exception did not apply because they did not install the Meta Pixel “for the distinct purpose of violating HIPAA or perpetrating a tort.” Id. at *11-12.

The Court’s Decision

The Court agreed with defendants and granted their motion to dismiss, holding that the amended complaint’s allegations “do not support the inference that Defendants purposefully committed the ‘criminal and tortious acts’ specified by Plaintiffs.” Id. at *13-14.

As the Court explained, based on the alleged predicate acts, plaintiffs were required to plausibly allege that defendants “purposefully used or caused to be used” plaintiffs’ unique health identifiers without authorization; “purposefully disclosed” plaintiffs’ individually identifiable health information to Facebook or Google without authorization; or “purposefully invaded” plaintiffs’ privacy.  Id. at *12-13.

Importantly, the Court emphasized that merely alleging that defendants knowingly committed such acts is insufficient because “‘purpose’ is an essential element of ECPA, distinct from the minimal intent [of knowingness] required under HIPAA.” Id. at *13 (quoting Doe v. Lawrence Gen. Hosp., 2025 U.S. Dist. LEXIS 195964, at *32 (D. Mass. Aug. 29, 2025)). The Court further explained that “[i]t is not enough that a crime or tort [may have been] a . . . side effect of the interception.” Id. at *14 (quoting Doe, 2025 U.S. Dist. LEXIS 195964, at *30).

Implications For Companies

The decision in Progin is a big win for healthcare providers and other defendants facing adtech class actions. This ruling reinforces a critical principle in ECPA and other privacy-based litigation: the defendants’ state of mind matters.

Under the ECPA’s HIPAA-based crime-tort exception, as well as under similar privacy statutes such as the Video Privacy Protection Act (“VPPA”), liability depends on the defendant’s knowledge and purpose. Where a defendant lacks knowledge that transmitted data is tied to specific individuals, or lacks the purpose to disclose identifiable information, the statutory requirements for liability may not be satisfied.

Accordingly, Progin provides strong authority for defendants to argue that routine adtech data transmissions cannot satisfy the purposeful intent requirements of the ECPA’s HIPAA-based crime-tort exception or similarly worded privacy statutes – a position that may prove critical as courts continue to confront the growing wave of adtech privacy class actions.

© 2009- Duane Morris LLP. Duane Morris is a registered service mark of Duane Morris LLP.

The opinions expressed on this blog are those of the author and are not to be construed as legal advice.

Proudly powered by WordPress