AbbVie Defeats Genetic Privacy Class Action Because Request For Plaintiff’s Family Medical History Was Not A “Condition Of Employment”

By Gerald L. Maatman, Jr., Tyler Zmick, and Hayley Ryan

Duane Morris Takeaways:  In Henry v. AbbVie, Inc., No. 23-CV-16830 (N.D. Ill. Mar. 20, 2026), Judge Manish S. Shah of the U.S. District Court for the Northern District of Illinois granted defendant’s motion for summary judgment and dismissed a claim brought under the Illinois Genetic Information Privacy Act (“GIPA”). In his ruling, Judge Shah determined that the alleged request for plaintiff’s family medical history (which history Plaintiff did not provide) during his pre-employment medical screening was not a “condition of employment.” The decision is welcome news for employers that ask employees to undergo medical exams. The ruling indicates that an employer does not necessarily request genetic information “as a condition of employment” by requiring an employee to undergo a medical exam (even if an employee is asked to disclose genetic information during the exam).

Background

Plaintiff Daniel Henry was assigned to work for Defendant AbbVie, Inc., a biopharmaceutical company. During the onboarding process, Plaintiff was required to undergo a “medical surveillance,” which included “questionnaires, blood work, and a brief physical exam.” Henry v. AbbVie, Inc., 2026 WL 788630, at *2 (N.D. Ill. Mar. 20, 2026).

AbbVie used Premise Health, a third-party healthcare provider, to conduct Plaintiff’s medical screening. During the screening, Premise Health nurses asked Plaintiff to complete a written questionnaire and to undergo a physical examination. “Section U” of the questionnaire asked for Plaintiff’s genetic information (specifically, his family medical history), though Plaintiff did not complete that part of the form. Plaintiff claimed that nurses also verbally asked for his family medical history during the physical exam. After the exam, Plaintiff worked at an AbbVie facility in Illinois for four months.

Plaintiff subsequently sued AbbVie under the GIPA, alleging that the company violated Section 25(c)(1) of the statute by “solicit[ing], request[ing], [or] requir[ing] . . . genetic information of a person or a family member of the person . . . as a condition of employment [or] preemployment application.”  410 ILCS 513/25(c)(1).

AbbVie first responded to Plaintiff’s Complaint by moving to dismiss under Federal Rule of Civil Procedure 12(b)(6). Judge Shah denied AbbVie’s motion to dismiss after determining that the family medical history information sought during the medical screening constituted “genetic information” under the GIPA. See Henry v. AbbVie, Inc., 2024 WL 4278070, at *5-6 (N.D. Ill. Sept. 24, 2024).

AbbVie later moved for summary judgment, arguing that: (1) AbbVie did not request Plaintiff’s genetic information because third-party Premise Health (not AbbVie) conducted the screening; (2) even if AbbVie requested Plaintiff’s genetic information, the request was inadvertent because the medical questionnaire instructed Plaintiff to not disclose genetic information; and (3) AbbVie did not condition Plaintiff’s work status or assignment on any request for his genetic information.

The Court’s Decision

The Court granted AbbVie’s motion for summary judgment. While the Court was not persuaded by AbbVie’s first two arguments, it concluded that AbbVie’s third argument warranted dismissal of Plaintiff’s GIPA claim.

Request for Genetic Information

The Court first considered whether AbbVie can be characterized as having requested Plaintiff’s family medical history despite third-party Premise Health having conducted the medical screening. In answering in the affirmative, the Court relied on the GIPA’s incorporation of certain protections found in the federal Genetic Information Nondiscrimination Act (“GINA”). See 410 ILCS 513/25(a) (“An employer … shall treat genetic testing and genetic information in such a manner that is consistent with the requirements of federal law, including but not limited to [GINA].”). The Court cited a regulation promulgated under GINA providing that an employer that requires employees or applicants to undergo medical examinations “must tell health care providers not to collect genetic information, including family medical history, as part of a medical examination intended to determine the ability to perform a job.” 29 C.F.R. § 1635.8(d). Based on this federal regulation, the Court concluded that AbbVie “[n]ot telling Premise Health to elicit genetic information is not enough; the [GIPA] requires an affirmative instruction not to elicit it.” Henry, 2026 WL 788630, at *5.

Inadvertent Disclosure

AbbVie’s second argument turned on the GIPA’s “inadvertent exception,” which states that “inadvertently requesting family medical history by an employer … does not violate this Act.” 410 ILCS 513/25(g). The Court observed that AbbVie’s health questionnaire advised Plaintiff to “not provide any genetic information, including family medical history.” Henry, 2026 WL 788630, at *6 (citation omitted). Thus, the Court held that the inadvertent exception barred Plaintiff’s claim to the extent it was premised on the written questionnaire. See id. (“The disclaimer on AbbVie’s form was enough to make any disclosure on the form inadvertent.”). But the Court determined that the exception did not necessarily bar Plaintiff’s claim to the extent it was premised on nurses orally asking for his family medical history. See id. (“[T]he written disclaimer in the form does not necessarily mean that [Plaintiff] knew that he should not disclose genetic information in response to verbal questions during his physical exam.”) (emphasis added).

Request as a Condition of Employment

Finally, the Court turned to AbbVie’s argument that Plaintiff’s claim failed because any request for his family medical history was not a condition of his employment. See 410 ILCS 513/25(c)(1) (an employer may not “solicit, request, [or] require … genetic information of a person or a family member of the person … as a condition of employment [or] preemployment application”) (emphasis added). The Court agreed with AbbVie and granted the company’s motion for summary judgment on this basis, holding that no genuine issue of material fact existed regarding AbbVie’s request for Plaintiff’s family medical history not having been a condition of his employment. The Court further noted that “the request for genetic information on the written questionnaire was not a condition of [Plaintiff’s] employment, for the simple fact that [Plaintiff] did not fill out that section and it did not affect his employment with AbbVie.” Henry, 2026 WL 788630, at *6.

Moreover, the Court concluded that even if Plaintiff was required to undergo a medical exam to be eligible to work at AbbVie, that did not mean that the verbal request for his family medical history (made during the exam) was a condition of his employment. See id. at *7. The Court thus recognized an important distinction between (i) AbbVie requiring Plaintiff to undergo a medical screening as a condition of employment and (ii) AbbVie specifically requesting Plaintiff’s family medical history as a condition of employment. See id. (“[T]hat [Plaintiff] could not decline to complete his medical surveillance does not create a genuine dispute over whether the verbal request during his exam was a condition of his employment. The undisputed evidence is that a contractor could decline parts of the surveillance and still have the surveillance considered completed.”). Accordingly, because AbbVie did not condition Plaintiff’s employment on a request for his genetic information, the Court granted summary judgment in the company’s favor.

Takeaways For Companies

As noted in a prior blog post, recent decisions suggest that courts may be hesitant to dismiss GIPA claims (especially at the pleading stage). Given the GIPA statute’s strict penalty provision – under which statutory damages can quickly become significant ($2,500 per negligent violation and $15,000 per intentional or reckless violation, see 410 ILCS 513/40(a)(1)-(2)) – we have advised employers to ensure they comply with the statute regarding any health screenings they ask applicants or employees to complete (including by explicitly advising applicants and employees not to disclose their family medical histories during the screenings).

In this plaintiff-friendly litigation landscape, the Henry decision comes as welcome news for GIPA defendants and companies that have employees undergo medical screenings. Importantly, Henry suggests that an employer does not necessarily violate the GIPA by requesting an employee’s genetic information “as a condition of employment” by merely directing her to undergo a medical exam (during which the employee may or may not be asked to provide her family medical history).
Massachusetts Federal Court Dismisses Adtech ECPA Class Action For Failure To Allege Defendants Purposefully Committed A Criminal Act, Furthering Split Of Authority

By Gerald L. Maatman, Jr., Justin Donoho, and Hayley Ryan

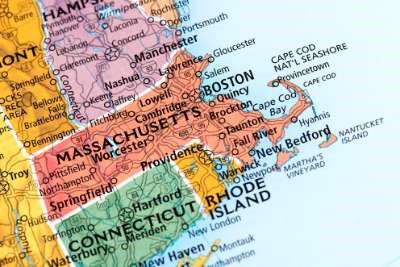
Duane Morris Takeaways: On March 6, 2026, in Progin v. UMass Memorial Health Care, Inc., No. 25-CV-40003, 2026 U.S. Dist. LEXIS 46522 (D. Mass. Mar. 6, 2026), Judge Allison D. Burroughs of the U.S. District Court for the District of Massachusetts granted a motion to dismiss a class action complaint brought by website users against Massachusetts health care and hospital entities. Plaintiffs alleged that the defendants’ use of website advertising technology (“adtech”) violated the federal Wiretap Act, also known as the Electronic Communications Privacy Act (“ECPA”).  Following another similar ruling in the same court,  see Goulart v. Cape Cod Healthcare, Inc., 2025 U.S. Dist. LEXIS 119435 (D. Mass. June 24, 2025),  the decision is significant because it reflects the Massachusetts Federal court’s alignment with other federal courts (including the U.S. District Court for the Southern District of Texas, as we blogged about here) that have interpreted the ECPA in a defense-friendly manner. In contrast, courts in other jurisdictions (including Illinois Federal courts, as we blogged about here) have adopted more plaintiff-friendly interpretations, further deepening the emerging split of authority in adtech privacy litigation.

Background

Progin is one of a legion of class actions that plaintiffs have filed nationwide alleging that Meta Pixel, Google Analytics, and other similar software embedded in websites secretly captured plaintiffs’ web-browsing data and transmitted that data to Meta, Google, and other online advertising agencies and data analytics companies.

In these adtech and similar internet-based technology class actions, plaintiffs frequently rely on the ECPA’s statutory damages provision. Their theory is simple: multiply the number of website visitors – potentially hundreds of thousands – by $10,000 in statutory damages per claimant to produce enormous potential exposure. Although plaintiffs have filed a majority of these lawsuits to date against healthcare providers, they have filed suits against companies that span nearly every industry including education, retailers, and consumer products. Some of these cases have resulted in multimillion-dollar settlements, while others have been dismissed at the pleading stage (as we blogged about here) or the summary judgment stage (as we blogged about here), and the vast majority remain undecided.

In Progin, the plaintiffs sued a group of health care and hospital entities, seeking to represent a class of patients whose personal health information was allegedly disclosed by the Meta Pixel installed on defendants’ websites. The plaintiffs claimed that these alleged transmissions constituted an “interception” by defendants in violation of the ECPA.

Under the ECPA, a “party to the communication” generally cannot be sued unless it intercepted the communication “for the purpose of committing any criminal or tortious act.” 18 U.S.C. § 2511(2)(d). This provision is commonly referred to as the “crime-tort exception.”

Plaintiffs argued that alleged violations of the Health Insurance Portability and Accountability Act (HIPAA) served as the predicate crime to trigger this exception. Specifically, plaintiffs argued that defendants were liable under the crime-tort exception because they intercepted and disclosed plaintiffs’ communications and personal information to third parties without consent in violation of HIPAA. 2026 U.S. Dist. LEXIS 46522, at *11.

The defendants moved to dismiss, arguing that the crime-tort exception did not apply because they did not install the Meta Pixel “for the distinct purpose of violating HIPAA or perpetrating a tort.” Id. at *11-12.

The Court’s Decision

The Court agreed with defendants and granted their motion to dismiss, holding that the amended complaint’s allegations “do not support the inference that Defendants purposefully committed the ‘criminal and tortious acts’ specified by Plaintiffs.” Id. at *13-14.

As the Court explained, based on the alleged predicate acts, plaintiffs were required to plausibly allege that defendants “purposefully used or caused to be used” plaintiffs’ unique health identifiers without authorization; “purposefully disclosed” plaintiffs’ individually identifiable health information to Facebook or Google without authorization; or “purposefully invaded” plaintiffs’ privacy.  Id. at *12-13.

Importantly, the Court emphasized that merely alleging that defendants knowingly committed such acts is insufficient because “‘purpose’ is an essential element of ECPA, distinct from the minimal intent [of knowingness] required under HIPAA.” Id. at *13 (quoting Doe v. Lawrence Gen. Hosp., 2025 U.S. Dist. LEXIS 195964, at *32 (D. Mass. Aug. 29, 2025)). The Court further explained that “[i]t is not enough that a crime or tort [may have been] a . . . side effect of the interception.” Id. at *14 (quoting Doe, 2025 U.S. Dist. LEXIS 195964, at *30).

Implications For Companies

The decision in Progin is a big win for healthcare providers and other defendants facing adtech class actions. This ruling reinforces a critical principle in ECPA and other privacy-based litigation: the defendants’ state of mind matters.

Under the ECPA’s HIPAA-based crime-tort exception, as well as under similar privacy statutes such as the Video Privacy Protection Act (“VPPA”), liability depends on the defendant’s knowledge and purpose. Where a defendant lacks knowledge that transmitted data is tied to specific individuals, or lacks the purpose to disclose identifiable information, the statutory requirements for liability may not be satisfied.

Accordingly, Progin provides strong authority for defendants to argue that routine adtech data transmissions cannot satisfy the purposeful intent requirements of the ECPA’s HIPAA-based crime-tort exception or similarly worded privacy statutes – a position that may prove critical as courts continue to confront the growing wave of adtech privacy class actions.

Hot Off The Presses! The Duane Morris Data Breach Class Action Review – 2026 And The Duane Morris Privacy Class Action Review – 2026!

By Gerald L. Maatman, Jr. and Jennifer A. Riley

Duane Morris Takeaways: Data breaches are becoming increasingly common and detrimental to companies. The scale of data breach class actions continued its record growth in 2025, as companies faced copycat and follow-on lawsuits across multiple jurisdictions. The last year also saw a virtual explosion in privacy class action litigation. As a result, compliance with privacy and data privacy laws in the myriad of ways that companies interact with employees, customers, and third parties is a corporate imperative.

To that end, the class action team at Duane Morris is pleased to present the third editions of the Data Breach Class Action Review – 2026 and the Privacy Class Action Review – 2026. These publications analyze the key data breach and privacy-related rulings and developments in 2025 and the significant legal decisions and trends impacting data breach and privacy class action litigation for 2026. We hope that companies and employers will benefit from this resource and assist them with their compliance with these evolving laws and standards.

Click here to download a copy of the Duane Morris Data Breach Class Action Review – 2026 eBook.

Click here to download a copy of the Duane Morris Privacy Class Action Review – 2026 eBook.

Stay tuned for more data breach and privacy class action analysis coming soon on our weekly podcast, the Class Action Weekly Wire.

Third Circuit Affirms Dismissal Of CIPA Adtech Class Action Because A Party To A Communication Cannot Eavesdrop On Itself

By Gerald L. Maatman, Jr., Justin R. Donoho, Hayley Ryan, and Ryan Garippo

Duane Morris Takeaways:  On November 13, 2025, in Cole, et al. v. Quest Diagnostics, Inc., 2025 U.S. App. LEXIS 29698 (3d Cir. Nov. 13, 2025), the U.S. Court of Appeals for the Third Circuit affirmed a ruling of the U.S. District Court for the District of New Jersey’s in dismissing a class action complaint brought by website users against a diagnostic testing company alleging that the company’s use of website advertising technology violated the California Invasion of Privacy Act (“CIPA”) and California’s Confidentiality of Medical Information Act (“CMIA”). 

The ruling is significant because it confirms two important principles: (1) CIPA’s prohibition against eavesdropping does not apply to an online advertising company, like Facebook, when it directly receives information from the users’ browser; and (2) the CMIA is not triggered unless plaintiffs plausibly allege the disclosure of substantive medical information.

Background

This case is one of a legion of nationwide class actions that plaintiffs have filed alleging that third-party technologies (“adtech”) captured user information for targeted advertising. These tools, such as the Facebook Tracking Pixel, are widely used across millions of consumer products and websites.

In these cases, plaintiffs typically assert claims under federal or state eavesdropping statutes, consumer protection laws, or other privacy statutes. Because statutes like CIPA allow $5,000 in statutory damages per violation, plaintiffs frequently seek millions, or even billions, in potential recovery, even from midsize companies, on the theory that hundreds of thousands of consumers or website visitors, times $5,000 per claimant, equals a huge amount of damages. While many of these suits initially targeted healthcare providers, plaintiffs have sued companies across nearly every industry, including retailers, consumer products companies, universities, and the adtech companies themselves.

Several of these cases have resulted in multimillion-dollar settlements; others have been dismissed at the pleading stage (as we blogged about here) or at the summary judgment stage (as we blogged about here and here). Still, most remain undecided, and with some district courts allowing adtech class actions to survive motions to dismiss (as we blogged about here), the plaintiffs’ bar continues to file adtech class actions at an aggressive pace.

In Cole, the plaintiffs alleged that the defendant diagnostic testing company used the Facebook Tracking Pixel on both its general website and its password-protected patient portal.  Id. at *1-2.  According to the plaintiffs, when a user accessed the general website, the Pixel intercepted and transmitted to Facebook “the URL of the page requested, along with the title of the page, keywords associated with the page, and a description of the page.” Id. at *2-3. Likewise, when a user accessed the password-protected website, the Pixel allegedly transmitted the URL “showing, at a minimum, that a patient has received and is accessing test results.” Id. at *3.

Plaintiffs asserted that these transmissions constituted (1) a CIPA violation because the company supposedly aided Facebook in “intercepting” plaintiffs’ internet communications, and (2) a CMIA violation because the company allegedly disclosed URLs associated with webpages plaintiffs accessed to view test results along with plaintiffs’ identifying information linked to users’ Facebook accounts. Id. at *3.

The company moved to dismiss, and, in separate orders, the district court dismissed both claims. See 2024 U.S. Dist. LEXIS 116350; 2025 U.S. Dist. LEXIS 7205.

As to the CIPA claim, the district court found that CIPA “is aimed only at ‘eavesdropping, or the secret monitoring of conversations by third parties,’” and that Facebook was not a third party because it received information directly from plaintiffs’ browsers about webpages they visited. 2025 U.S. Dist. LEXIS 7205, at *7-8 (quoting In Re Google Inc. Cookie Placement Consumer Privacy Litig., 806 F.3d 125, 140-41 (3d Cir. 2015)).  As to the CMIA claim, the district court found that plaintiffs alleged only that the company disclosed that a patient accessed test results but not what kind of medical test was done or what the results were. 2024 U.S. Dist. LEXIS 116350, at *15. Accordingly, the district court held that plaintiffs failed to allege the disclosure of “substantive” medical information as required under the CMIA. Id.

Plaintiffs appealed both rulings.

The Court’s Decision

The Third Circuit affirmed. Id. at *1.

On the CIPA claim, the Third Circuit explained that “[a]s a recipient of a direct communication from Plaintiffs’ browsers, Facebook was a participant in Plaintiffs’ transmissions such that [the company] did not aid or assist Facebook in eavesdropping on or intercepting such communications, even if done without the users’ knowledge.” 2025 U.S. App. LEXIS 29698, at *6.  With no eavesdropping, “Plaintiffs’ CIPA claim was properly dismissed.” Id. at *7.

On the CMIA claim, the Third Circuit explained that “at most, Plaintiffs alleged that [the company] disclosed Plaintiffs had been its patients, which is not medical information protected by CMIA.” Id. at *8. Thus, the Third Circuit held that the district court properly dismissed the CMIA claim. Id. at *9.

Implications For Companies

Cole offers strong precedent for any company defending adtech class action claims (1) brought under CIPA’s eavesdropping provision where the third-party adtech company directly receives the information from users’ browsers and (2) brought under the CMIA where the alleged disclosure merely shows that a person was a patient, without revealing any substantive information about the person’s medical condition or test results.

The latter point continues to appear across adtech class actions.  Just as the plaintiffs in Cole failed to plausibly allege the disclosure of substantive medical information,  courts have dismissed similar claims where plaintiffs allege disclosure of protected health information (“PHI”) without actually identifying what PHI was supposedly shared (as we blogged about here).  These decisions reinforce that adtech plaintiffs must identify the specific medical information allegedly disclosed to plausibly plead claims under the CMIA or for invasion of privacy.

California Federal Court Dismisses Adtech Class Action For Failure To Specify Highly Offensive Invasion Of Privacy

By Gerald L. Maatman, Jr., Justin R. Donoho, Tyler Zmick, and Hayley Ryan

Duane Morris Takeaways:  On October 30, 2025, in DellaSalla, et al. v. Samba TV, Inc., 2025 WL 3034069 (N.D. Cal. Oct. 30, 2025), Judge Jacqueline Scott Corley of the U.S. District Court for the Northern District of California dismissed a complaint brought by TV viewers against a TV technology company alleging that the company’s provision of advertising technology in the plaintiffs’ smart TVs committed the common law tort of invasion of privacy and violated the Video Privacy Protection Act (“VPPA”), the California Invasion of Privacy Act (“CIPA”), and California’s Comprehensive Computer Data Access and Fraud Act (“CDAFA”).  The ruling is significant as it shows that in the hundreds of adtech class actions across the nation alleging that adtech violates privacy laws, plaintiffs do not plausibly state a common law claim for invasion of privacy unless they specify in the complaint the information allegedly disclosed and explain how such a disclosure was highly offensive.  The case is also significant in that it shows that the VPPA does not apply to video analytics companies, and that California privacy statutes do not apply extraterritorially to plaintiffs located outside California.

Background

This case is one of a legion of class actions that plaintiffs have filed nationwide alleging that third-party technology captured plaintiffs’ information and used it to facilitate targeted advertising. 

This software, often called advertising technologies or “adtech,” is a common feature of millions of consumer products and websites in operation today.  In adtech class actions, the key issue is often a claim brought under a federal or state wiretap act, a consumer fraud act, or the VPPA, because plaintiffs often seek millions (and sometimes even billions) of dollars, even from midsize companies, on the theory that hundreds of thousands of consumers or website visitors, times $2,500 per claimant in statutory damages under the VPPA, for example, equals a huge amount of damages.  Plaintiffs have filed the bulk of these types of lawsuits to date against healthcare providers, but they have filed suits against companies that span nearly every industry including retailers, consumer products, universities, and the adtech companies themselves.  Several of these cases have resulted in multimillion-dollar settlements, several have been dismissed, and the vast majority remain undecided. 

In DellaSalla, the plaintiffs brought suit against a TV technology company that embedded a chip with analytics software in plaintiffs’ smart TVs.  Id. at *1, 5.  According to the plaintiffs, the company intercepted the plaintiffs’ “private video-viewing data in real time, including what [t]he[y] watched on cable television and streaming services,” and tied this information to each plaintiff’s unique anonymized identifier in order to “facilitate targeted advertising,” all allegedly without the plaintiffs’ consent.  Id. at *1.  Based on these allegations, the plaintiffs claimed that the TV technology company violated the CIPA, CDAFA, and VPPA, and committed the common-law tort of invasion of privacy. 

The company moved to dismiss, arguing that the CIPA and CDAFA did not apply because the plaintiffs were located outside California, that the VPPA did not apply because the TV technology company was not a “video tape service provider,” and that the plaintiffs failed to plausibly allege a highly offensive violation of a privacy interest.

The Court’s Decision

The Court agreed with the TV technology company and dismissed the complaint in its entirety, with leave to amend any existing claims but not to add any additional claims without further leave.

On the CIPA and CDAFA claims, the Court found that the plaintiffs did not allege that any unlawful conduct occurred in California.  Instead, the plaintiffs alleged that the challenged conduct occurred in their home states of North Carolina and Oklahoma.  Id. at *1, 3-4.  For these reasons, the Court dismissed the CIPA and CDAFA claims, finding that these statutes do not apply extraterritorially.  Id.

On the VPPA claim, the Court addressed the VPPA’s definition of  “video tape service provider,” which is “any person, engaged in the business … of rental, sale, or delivery of prerecorded video cassette tapes or similar audio visual materials.”  Id. at *5.  The plaintiffs argued that the TV technology company was a video tape service provider “because its technology is incorporated in Smart TVs, which deliver prerecorded videos.  [The defendant] advertises its technology precisely as providing a ‘better viewing experience’ ‘immersive on-screen experiences’ and a ‘more tailored ad experience’ through its technology.”  Id.  The Court rejected this argument. It held that “[t]his allegation does not plausibly support an inference, [the defendant]—an analytics software provider—facilitated the exchange of a video product. Rather, the allegations support an inference [the defendant] collected information about Plaintiffs’ use of a video product, but not that it provided the product itself.”  Id. (emphasis added).

On the common law claim for invasion of privacy, the TV technology company argued that this claim failed because the plaintiffs “have no expectation of privacy in the information it collects and Plaintiffs have not alleged a highly offensive intrusion.”  In examining this argument, the Court noted that Plaintiff had only provided “vague references” to the information supposedly intercepted.  Id. at *4.  This information included video-viewing data generally (none specified) tied to an anonymized identifier.  Id. at *1, 5.  Thus, the Court agreed with the defendant’s argument and found that plaintiffs identified “no embarrassing, invasive, or otherwise private information collected” and no explanation of how the tracking of video viewing history with an anonymized ID caused plaintiffs “to experience any kind of harm that is remotely similar to the ‘highly offensive’ inferences or disclosures that were actionable at common law.”  Id. at *5.  In sum, the Court concluded that “Plaintiffs have not plausibly alleged a highly offensive violation of a privacy interest.”

Implications For Companies

DellaSala provides powerful precedent for any company opposing adtech class action claims (1) brought under statutes enacted in states other than the plaintiffs’ place of residence; (2) brought under the federal VPPA where the company allegedly transmitted video usage information, as opposed to any videos themselves; and (3) alleging common-law invasion of privacy, where the plaintiffs have not specified the information disclosed and why such a disclosure is highly offensive. 

The last point is a recurring theme in adtech class actions.  Just as this plaintiff suing a TV technology company did not plausibly state a common-law claim for invasion of privacy without identifying the videos watched and any highly offensive harm in associating those videos with an anonymized ID, so did a plaintiff not plausibly state a claim for invasion of privacy by way of alleging adtech’s disclosure of protected health information (“PHI”), without specifying the PHI allegedly disclosed (as we blogged about here).  These cases show that for adtech plaintiffs to plausibly plead claims for invasion of privacy, they at least need to identify what allegedly private information was disclosed and explain how the alleged disclosure was highly offensive.

California Federal Court Narrows CIPA “In-Transit” Liability for Common Website Advertising Technology and Urges Legislature to Modernize Privacy Law

By Gerald L. Maatman, Jr., Justin Donoho, Hayley Ryan, and Tyler Zmick

Duane Morris Takeaways: On October 17, 2025, in Doe v. Eating Recovery Center LLC, No. 23-CV-05561, ECF 167 (N.D. Cal. Oct. 17, 2025), Judge Vince Chhabria of the U.S. District Court for the Northern District of California granted summary judgment to Eating Recovery Center, finding no violation of the California Invasion of Privacy Act (CIPA) where the Meta Pixel collected website event data. Specifically, the Court held that Meta did not “read” those contents while the communications were “in transit.” In so holding, the Court applied the rule of lenity, construed CIPA narrowly, and urged the California Legislature “to step up” and modernize the statute for the digital age. Id. at 2.

This decision is significant because Judge Chhabria candidly described CIPA as “a total mess,” noting it is often “borderline impossible” to determine whether the law – enacted in 1967 to criminalize wiretapping and eavesdropping on confidential communications – applies to modern internet transmissions. Id. at 1. As the Court observed, CIPA “was a mess from the get-go, but the mess gets bigger and bigger as the world continues to change and as courts are called upon to apply CIPA’s already-obtuse language to new technologies.” Id.  This is a “must read” decision for corporate counsel dealing with privacy issues and litigation.

Background

This class action arose after plaintiff, Jane Doe, visited Eating Recovery Center’s (ERC) website to research anorexia treatment and later received targeted advertisements. Plaintiff alleged that ERC’s use of the Meta Pixel caused Meta to receive sensitive URL and event data from her interactions with ERC’s site, resulting in targeted ads related to eating disorders.

ERC had installed the standard Meta Pixel on its website, which automatically collected page URLs, time on page, referrer paths, and certain click events to help ERC build custom audiences for advertising. Id. at 3. Plaintiff alleged that ERC’s use of the Pixel allowed Meta to intercept her communications in violation of CIPA, Cal. Penal Code § 631(a). She also brought claims under the California Medical Information Act (CMIA), the California Unfair Competition Law (UCL), and for common law unjust enrichment. The UCL claim was dismissed at the pleading stage.

ERC later moved for summary judgment on the remaining CIPA, CMIA, and unjust enrichment claims. In a separate order, the Court granted summary judgment on the CMIA and unjust enrichment claims, finding that plaintiff was not a “patient” under the CMIA and that there was no evidence ERC had been unjustly enriched. See id., ECF 168 at 1-2.

The Court’s Decision

With respect to the CIPA claim, the parties disputed two elements under CIPA § 631(a): (1) whether the event data obtained by Meta constituted “contents” of plaintiff’s communication with ERC, and (2) whether Meta read, attempted to read, or attempted to learn those contents while they were “in transit.” ECF 167 at 6.

The Court first held that URLs and event data can constitute the “contents” of a communication because they can reveal substantive information about a user’s activities – such as researching medical treatment. Id. at 7. The court thus deviated from other courts that have held differently on this particular issue when considering additional facts or allegations not addressed by this court (such as encryption, and inability to reasonably identify the data among lines of code).  However, the Court concluded that Meta did not read or attempt to learn any contents while the communications were “in transit.” Instead, Meta processed the data only after it had reached its intended recipient (i.e., ERC, the website operator).

In reaching that conclusion, Judge Chhabria relied on undisputed testimony about Meta’s internal filtering processes: “Meta’s corporate representative testified that, before logging the data that it obtains from websites, Meta filters URLs to remove information that it does not wish to store (including information that Meta views as privacy protected).” Id. at 8.

This evidence supported the finding that Meta’s conduct involved post-receipt filtering rather than contemporaneous “reading” or “learning.” Id. at 9. The Court emphasized that expanding “in transit” to include post-receipt processing would improperly criminalize routine website analytics practices. Because CIPA is both a criminal statute and a source of punitive civil penalties, the Court applied the rule of lenity to adopt a narrow interpretation. Id. at 11-12. The Court further cautioned that an overly broad reading would render CIPA’s related provision (§ 632, prohibiting eavesdropping and recording) largely redundant. Id. at 10.

Finding that Meta did not read, attempt to read, or attempt to learn the contents of Doe’s communications while they were in transit, the court granted summary judgment to ERC on the CIPA claim. Id. at 12.

The opinion concluded by reiterating that California’s decades-old wiretap law is “virtually impossible to apply [] to the online world,” urging the Legislature to “go back to the drawing board on CIPA,” and suggesting that it “would probably be best to erase the board entirely and start writing something new.” Id.

Implications For Companies

The Doe decision narrows one significant avenue for CIPA liability, particularly for routine use of website analytics and advertising pixels. The Northern District of California has now drawn a distinction between data “read” while in transit and data processed after receipt, significantly reducing immediate CIPA exposure for standard web advertising tools.

At the same time, the court’s reasoning underscores that pixel-captured data may be considered by some courts as “contents” of a communication under CIPA, although there is a split of authority on this issue. Companies could therefore face potential exposure under other California privacy statutes, including the CMIA, the California Consumer Privacy Act (CCPA), and the California Privacy Rights Act (CPRA), depending on the data involved and how it is used.

Organizations should continue to inventory the data they share through advertising technologies, minimize sensitive information in URLs, and ensure clear and accurate privacy disclosures. Because the court expressly invited legislative reform, companies should also monitor ongoing case law and potential statutory amendments.

Ultimately, Doe v. Eating Recovery Center reflects a pragmatic narrowing of CIPA’s “in transit” requirement while reaffirming that CIPA was not intended to cover common website advertising technologies or, in any event, should not be interpreted as such given the harsh statutory penalties involved and the rule of lenity — like the Supreme Judicial Court of Massachusetts concluded regarding Massachusetts’ wiretap act, as we previously blogged about here.  While this case is a big win for website operators, companies relying on third-party analytics should treat this decision as guidance—not immunity—and continue adopting privacy-by-design principles in their data collection and vendor management practices.

The NBA Sinks The Second Shot: New York Federal Court Grants Second Motion To Dismiss In Putative Privacy Class Action

By Gerald L. Maatman, Jr., Ryan T. Garippo, and Elizabeth G. Underwood

Duane Morris Takeaways: On October 6, 2025, in Salazar v. National Basketball Association, No. 22 Civ. 07935, 2025 WL 2830939 (S.D.N.Y. Oct. 6, 2025), Judge Jennifer L. Rochon of the U.S. District Court for the Southern District of New York dismissed a proposed digital privacy class action against the National Basketball Association (“NBA”) because the plaintiff failed to plausibly allege that the NBA disclosed personally identifiable information in violation of the Video Privacy Protection Act (“VPPA”).  The district court reasoned that, following Second Circuit precedent, an “ordinary person” would not be able to identify the plaintiff’s video-watching habits from the alleged Pixel transmissions.  Id. at *5.  This ruling illustrates that district courts in the Second Circuit continue to interpret the phrase “personally identifiable information” contained within the VPPA narrowly, and that the uphill burdens that plaintiffs carry on adtech and VPPA claims against corporate defendants are continuing to grow steeper.

Case Background

In Salazar v. NBA,  the plaintiff, Michael Salazar (“Plaintiff”) alleged that the NBA disclosed his personal information, including personal viewing information, to Meta, the owner of Facebook and Instagram, via Meta Pixel (a common form of advertising technology or “adtech”).  Id. at *1–3.  According to Plaintiff, Meta Pixel is “a snippet JavaScript code” that allows online businesses to “track visitor activity on their website.”  Id. at *1.  When Meta Pixel is activated, it supposedly tracks the visitors and the visitors’ actions, including the pages they visit and the buttons they click.  Id.  Plaintiff filed his suit against the NBA on September 16, 2022.  Id. at *2.  He claimed that he signed up for an online newsletter to register for NBA.com and then that he separately watched videos on the NBA’s website.  Id. at *1.  Plaintiff also alleged that after he watched videos on the NBA’s website, not in connection with his subscription to the newsletter, his video-watching history was sent to Meta without his permission via the undisclosed use of Meta Pixel on the NBA’s website.  Id. at *5.  In response, the NBA filed a motion to dismiss and argued that Plaintiff failed to plead that he was a consumer of goods and services within the meaning of the VPPA, because although he alleged that he viewed audio-visual content on the NBA’s website, he did not allege that he viewed the materials that he actually subscribed to but rather, separate, and free content that was offered elsewhere on the website.  So, put differently, the content containing adtech was not the content that created his statutory standing to sue under the VPPA.  Id. at *2. 

The district court agreed with the NBA and granted its first motion to dismiss under Rule 12(b)(6).  Plaintiff, however, appealed the decision to the U.S. Court of Appeals for the Second Circuit.  On appeal, the Second Circuit agreed with Plaintiff, vacated the district court’s judgment, and remanded the case, finding that the plaintiff had “plausibly pleaded” that he was a consumer under the VPPA by alleging that he had subscribed to the NBA’s digital newsletter.  Id.  The Second Circuit reasoned that as long as the plaintiff was a “subscriber” under the meaning of the VPPA, he only needed to allege that he separately viewed audio-visual content offered by the defendant in order to state a valid claim.  The Duane Morris summary of the Second Circuit’s decision is attached here which describes the opinion in more detail.

Notably, this decision was not the only time that Plaintiff raised these issues to an appellate court.  In April, the U.S. Court of Appeals for the Sixth Circuit ruled against this exact same Plaintiff on the same issue, based on the argument that a plaintiff needed to subscribe to the audio-visual content he or she alleges was actually disclosed in order to have statutory standing to sue under the VPPA.  Thus, the Sixth Circuit created the odd situation where this exact same Plaintiff, Michael Salazar, filed one lawsuit in New York where he had statutory standing and another in Tennessee where he did not.  The Duane Morris summary of the Sixth Circuit’s decision is attached here and also provides more detail.

Nonetheless, on remand from the Second Circuit, Plaintiff filed a First Amended Complaint and later filed a Second Amended Complaint.  Id.  In response, the NBA again moved to dismiss the claims under Rule 12(b)(6), this time arguing that (1) pursuant to binding Second Circuit precedent, there was no disclosure of personally identifiable information under the VPPA; and (2) the plaintiff did not allege knowing disclosure.  Id. at *3.

The Court’s Opinion

Judge Rochon agreed with the NBA and dismissed Plaintiff’s proposed VPPA class action.  Id. at *5.  In reaching its decision, the Court applied the Second Circuit’s “ordinary person” standard, which requires plaintiffs to show that the “personally identifiable information” includes information that would permit an “ordinary person” to identify a user’s video-watching habits.  Id. at *3.

Under the standard, the Court found that the personally identifiable information would not allow an ordinary person to identify Plaintiff’s video-watching habits, relying on other cases in which the Second Circuit rejected Pixel-based VPPA claims that “mirror” the allegations at issue.  Id. at *3, *5; see Soloman v. Flipps Media, Inc., 136 F.4th 41, 44 (2d Cir. 2025) (finding that the complaint did not “plausibly allege that an ordinary person could identify [the plaintiff]” because an ordinary person would not be able to decipher the “c_user” cookie and corresponding string of letters to be a person’s Facebook ID); see also Hughes v. National Football League, 24-2656, 2025 WL 1720295 (2d Cir. June 20, 2025) (rejecting the argument that a user’s Facebook ID could be identified based on lines of computer code because it was not plausible that an ordinary person would conclude that the phrase was a person’s Facebook ID).  The Court aligned with other district court rulings in finding the plaintiff’s argument — that a person could use internet-based tools like ChatGPT to understand the code communication — to be unpersuasive, reasoning that the argument was “insufficient to demonstrate that an ordinary person would know what to do with the c_user information to pinpoint an individual’s identity.”  Id. at *5. (citing Taino v. Bow Tie Cinemas, LLC, No. 23-CV-0537, 2025 WL 2652730, at *8 (S.D.N.Y. Sept. 16, 2025)).

Although Plaintiff asked the Court not to dismiss the complaint based on the holdings in Soloman and Hughes, claiming the Soloman and Hughes line of precedent was on unstable footing, the Court independently concluded that “[t]here is no basis for this Court to find that the Second Circuit’s decision in Soloman runs afoul of the statutory text of the VPPA, and thus Plaintiff’s reliance on these [alternative] cases does not convince the Court that Soloman is soon to be overruled.”  Id. at *4.  In other words, “[b]ecause an ordinary person would not plausibly be able to identify Plaintiff’s video-watching habits as a result of the Pixel transmissions, Plaintiff has not plausibly alleged that the NBA disclosed personally identifiable information in violation of the VPPA.”  Id. at *5.

Implications For Companies

This case is a success for defendants involved in other putative adtech class actions.  Indeed, Salazar is another example of a district court applying a narrow interpretation of “personally identifiable information” under the Second Circuit’s “ordinary person” standard and has broader implications outside of the VPPA to adtech class actions generally.

As a result, if corporate counsel is faced with an adtech class action, based on common-place technology installed on his or her organization’s website, he or she should consider raising these arguments in a motion to dismiss or shortly thereafter, as Salazar and its progeny may prove to be a powerful tool to exit a putative class action early in the litigation.. 

Illinois Federal Court Finds “Self-Inflicted Injury” Insufficient To Confer Article III Standing In Publicity Class Action Lawsuit

By Gerald L. Maatman, Jr., Justin Donoho, Hayley Ryan, and Tyler Zmick

Duane Morris Takeaways: On October 2, 2025, in Azuz v. Accucom Corp. d/b/a InfoTracer, No. 21-CV-01182, 2025 U.S. Dist. LEXIS 195474 (N.D. Ill. Oct. 2, 2025), Judge LaShonda A. Hunt of the U.S. District Court for the Northern District of Illinois dismissed a class action complaint alleging violations of the Illinois Right of Publicity Act (IRPA). The plaintiff claimed that InfoTracer unlawfully used individuals’ names and likeness to advertise and promote its products without consent. The Court held that the Plaintiff lacked Article III standing because she failed to plausibly allege a concrete injury – her only alleged harm was “self-inflicted,” as no one other than her own counsel ever searched her name on the site.

The decision illustrates that plaintiffs bringing right of publicity claims against website operators must show that a third party actually accessed their information for a commercial purpose. Mere availability of an individual’s information on a website, without evidence of third-party viewing, does not establish a concrete injury under Article III.

Background

Plaintiff Marilyn Azuz filed a putative class action complaint against Accucom Corp. d/b/a InfoTracer, which operates infotracer.com, a website selling personal background reports. She alleged that Accucom used her name and likeness to advertise and promote its products without written consent, in violation of the IRPA. Id. at *2-4. Plaintiff sought damages and injunctive relief barring Accucom from continuing the alleged conduct. Id. at *4.

After three years of litigation and discovery, Accucom moved to dismiss for lack of subject matter jurisdiction, raising a factual challenge to Article III standing. Accucom submitted evidence showing that the only search of Plaintiff’s name on InfoTracer occurred in February 2021, when her own counsel accessed the site after she responded to a Facebook solicitation by her counsel about potential claims. Accucom argued that such a “self-inflicted” search could not establish a concrete injury and that Plaintiff’s claim for injunctive relief was moot because she had since moved to Minnesota and her data had been removed from the site.

Plaintiff countered that her identify being “held out” to be searched constituted a sufficient injury, and that her request for injunctive relief was not moot Accucom could resume the alleged conduct.

The Court’s Decision

The Court sided with Accucom, holding that the Plaintiff failed to establish a concrete injury and therefore lacked standing to pursue her individual claims. Id. at *15.

Relying on the U.S. Supreme Court’s decision in TransUnion LLC v. Ramirez, 594 U.S. 413 (2021), Judge Hunt explained that an intangible statutory violation, without evidence of concrete harm, is insufficient for Article III standing.  Just as inaccurate information in a credit file causes no concrete injury unless disclosed to a third party, the Court concluded, “a person’s identity is not appropriated under the IRPA unless it is used for a commercial purpose.” Id. at *14.

The Court rejected Plaintiff’s reliance on Lukis v. Whitepages Inc., 549 F. Supp. 3d 798 (N.D. Ill. 2021), noting that Lukis involved only a facial attack to standing at the pleading stage, not a factual attack supported by evidence, like here. Id. at *9-10.

Noting that it had not found any post-TransUnion decisions analyzing the IRPA under a factual challenge to standing, Judge Hunt found Fry v. Ancestry.com Operations Inc., 2023 U.S. Dist. LEXIS 50330 (N.D. Ind. Mar. 24, 2023) to be instructive. Id. at *11. In Fry, the court cautioned that a plaintiff asserting a right of publicity claim must ultimately produce evidence showing that his likeness was viewed by someone other than his attorney or their agents. That same “forewarning,” Judge Hunt concluded, applied to Plaintiff, who presented no such evidence. Id. at *12-13.

The Court also dismissed Plaintiff’s request for injunctive relief, holding that any potential future harm was speculative and not sufficiently imminent. Because Plaintiff had relocated to Minnesota, the IRPA’s extraterritorial application could not extend to her circumstances. Id. at *16.

Finally, the Court declined to allow the substitution of new named plaintiffs so that the case could continue, reasoning that because the original plaintiff lacked standing from the outset, the Court never had jurisdiction to allow substitution. Id. at *17.

Implications For Companies

Azuz underscores the importance of scrutinizing Article III standing in every stage of litigation, particularly in statutory publicity and privacy cases. Where plaintiffs cannot show that a third party viewed or interacted with their data, courts are likely to find no concrete injury — and therefore no federal jurisdiction.

Website operators facing IRPA or similar publicity-based class actions should consider asserting factual standing challenges supported by evidence demonstrating the absence of third-party access. Such jurisdictional defenses can be decisive and may be raised at any time in the litigation.

Hospital Defeats Wiretap Adtech Class Action After Texas Federal Court Finds No Knowing Disclosure Of Protected Health Information

By Gerald L. Maatman, Jr., Justin Donoho, and Hayley Ryan

Duane Morris Takeaways: On September 22, 2025, in Sweat v. Houston Methodist Hospital, No. 24-CV-00775, 2025 U.S. Dist. LEXIS 185310 (S.D. Tex. Sept. 22, 2025), Judge Lee H. Rosenthal of the U.S. District Court for the Southern District of Texas granted a motion for summary judgment in favor of a hospital accused of violating the federal Wiretap Act through its use of website advertising technology. This decision is significant. In the wave of adtech class actions seeking millions – sometimes billions – in statutory damages under the Wiretap Act and similar statutes, the Court held that the Act’s steep penalties (up to $10,000 per violation) were not triggered because the hospital did not knowingly transmit protected health information.

Background

This case is part of a rapidly growing line of class actions alleging that website advertising tools – such as the Meta Pixel, Google Analytics, and other similar website advertising technology, or “adtech,” –secretly capture users’ web-browsing activity and share it with third-party advertising platforms.

Adtech is ubiquitous, embedded on millions of websites. Plaintiffs’ lawyers frequently invoke the federal Wiretap Act, the Video Privacy Protection Act (VPPA), state invasion-of-privacy statutes like the California Invasion of Privacy Act (CIPA), and even the Illinois Genetic Information Privacy Act (GIPA). Their theory is straightforward: multiply hundreds of thousands of website visitors by $10,000 per alleged Wiretap Act violation and the potential damages skyrocket. While some of these class actions have resulted in multi-million-dollar settlements, others have been dismissed (as we blogged about here), and the vast majority remain pending. With some district courts allowing adtech class actions to survive motions to dismiss (as we blogged about here), the plaintiffs’ bar continues to file adtech class actions at an aggressive pace.

In Sweat, the plaintiffs sued a hospital, seeking to represent a class of patients whose personal health information was allegedly disclosed by the Meta Pixel installed on the hospital’s website. The district court granted the hospital’s motion to dismiss the state law invasion of privacy claim but allowed the Wiretap Act claim to proceed to discovery. The hospital then moved for summary judgment, arguing that the Wiretap Act’s crime-tort exception did not apply because the hospital lacked knowledge that it was disclosing protected health information.

Under the Wiretap Act, “party to the communication” cannot be sued unless it intercepted the communication “for the purpose of committing any criminal or tortious act.” 18 U.S.C. § 2511(2)(d). This provision is commonly called the “crime-tort exception.” The plaintiffs pointed to alleged violations of the Health Insurance Portability and Accountability Act (HIPAA) as the predicate crime to trigger this exception.

The Court’s Decision

The Court agreed with the hospital and granted summary judgment, holding that the record contained no evidence that the hospital acted with the “purpose of committing any criminal or tortious act” that would trigger the crime-tort exception. 2025 U.S. Dist. LEXIS 185310, at *13.

As the Court explained, case law authorities have developed two different approaches to determine “purpose” under the crime-tort exception. Some courts use the “independent act” approach, under which the unlawful act must be independent of the interception itself. Other courts have used the “primary purpose” approach, under which the defendant’s primary motivation must be to commit a crime or tort.

Applying the “primary purpose” approach, the Court found “no evidence that [the hospital] acted with the purpose of violating HIPAA…the evidence shows that it did not know it was doing so.” Id. at *13. In so holding, the Court cited to the fact that, although the Pixel was installed on “arguably sensitive portions” of the hospital’s website, the hospital received only aggregated, anonymized data, and there was no proof it knew any protected health information was being disclosed. Id. at *13-14. The Court rejected the plaintiffs’ argument that anonymized aggregate data necessarily originates from identifiable data, emphasizing that Meta’s algorithm could anonymize data “at the input level,” preventing the hospital from receiving identifiable data in the first place. Id. at *16.

Implications For Companies

The Court’s holding in Sweat is a significant win for healthcare providers and other defendants facing adtech class actions. This ruling reinforces two key principles. First, knowledge is critical. Like the Wiretap Act’s HIPAA-based crime-tort exception, similar statutes such as the VPPA require a knowing disclosure of identifiable information. If a defendant lacks knowledge that data is tied to specific individuals, liability should not attach. Second, anonymization matters. Where transmissions are encrypted, anonymized, or otherwise inaccessible at the point of input, there may be no “disclosure” at all.

For example, the VPPA requires disclosure of a person’s specific video-viewing activity, and GIPA requires disclosure of an identified individual’s genetic information. When adtech merely sends anonymized or encrypted data to third-party algorithms—data that cannot be traced back to a specific person—there is no knowing disclosure.

Sweat provides strong authority for defendants to argue that anonymized adtech transmissions cannot satisfy the statutory knowledge requirements of the Wiretap Act’s HIPAA-based crime-tort exception or similarly worded privacy statutes.

What The Click?:  Third Circuit Finds No Standing For Class Complaining Of Website Operator Monitoring Clicks 

By Gerald L. Maatman, Jr., Anna Sheridan, and Shannon Noelle

Duane Morris Takeaways: On August 7, 2025, in an opinion authored by Circuit Judge D. Michael Fisher, the United States Court of Appeals for the Third Circuit issued a precedential decision in Cook v. GameStop, Inc., 148 F.4th 153 (3d Cir. 2025), affirming the U.S. District Court for the Western District of Pennsylvania’s dismissal for lack of standing of a putative class action asserting privacy causes of action against a website operator monitoring clicks.  The Third Circuit found that merely tracking internet users’ browsing time and website interactions — without recording or disclosing sensitive or personal information — fails to constitute the type of concrete injury required to confer Article III standing.  The decision is instructive for corporate counsel dealing with privacy issues and defense of class action litigation.

Case Background

Plaintiff Amber Cook (“Cook” or “Plaintiff”) was an internet user that visited GameStop’s website in Pennsylvania.  See Cook, 148 F.4th 153, 156.  Through third-party vendor Microsoft and its programming script called Clarity, GameStop was tracking internet user’s browsing history and interaction with its website.  Id.  The script Clarity creates is known as a “session replay code” that aggregates data about how long the user browsed the website, mouse movement, links clicked, scrolling, search bar entries, and products added and removed from the “cart.”   Id.  The script creates a unique id and profile for each user and recaptures each user’s session through a video which GameStop could review to improve functionality and user experience.  Id.  The unique ids and profiles do not utilize personally identifying information such as names, addresses, and the like.  Id. at 160.  GameStop’s website has a privacy policy describing the script and information collected but this policy is “buried at the very bottom of the website.”   Id. at 156.

Cook sued GameStop for its use of the Clarity script, alleging that it violated the Pennsylvania Wiretapping and Electronic Surveillance Control Act (“WESCA”) and asserting a common law cause of action for intrusion upon seclusion.  Cook alleged that the WESCA and privacy tort for intrusion upon seclusion prohibit the interception of electronic communications without prior consent and she suffered an injury in fact “‘‘when her communications with . . . GameStop’s website were intercepted’ by the session replay code.”   GameStop moved to dismiss the First Amended Complaint at the District Court level pursuant to Federal Rule of Civil Procedure 12(b)(6) and 12(b)(1).  See Case No. 2:22-CV-01292, ECF No. 25-27.  The District Court granted GameStop’s motion under Rule 12(b)(1) with prejudice and, in the alternative, held that Cook failed to “plead the necessary facts to support her claims for violation of [WESCA] or intrusion upon seclusion.”  See Case No. 2:22-CV-01292, ECF No. 45-46.  Specifically, the District Court concluded that Cook’s harms were not analogous to the traditional intangible harms recognized by privacy torts because none of the data gathered “could connect her browsing activity to her.”   See Case No. 2:22-cCV01292, ECF No. 46, at 8 (emphasis in the original).  Cook appealed the District Court’s decision on standing to the Third Circuit.

The Third Circuit’s Ruling

Reviewing whether Cook’s allegations met the Article III standing threshold de novo, the Third Circuit determined that the appeal concerned only the first element of the analysis, or whether Cook had sufficiently alleged an injury in fact (as opposed to the other requirements of traceability and redressability).  The Third Circuit adopted the standard articulated in Barclift and Transunion that — to determine whether a plaintiff has suffered a concrete injury — the framework is whether the harm asserted bears a “close relationship to a harm traditionally recognized as providing a basis for a lawsuit in American courts — such as physical harm, monetary harm, or various intangible harms including . . . reputational harm.”  Id. at 158 (citing Barclift v. Keystone Credit Servs., LLC, 93 F.4th 136, 141, 145 (3d Cir. 2024); TransUnion LLC v. Ramirez, 594 U.S. 413, 417 (2021)). 

The Third Circuit clarified that it would not take as “rigid” of an approach as other federal circuits but that it would consider the privacy torts that Cook identified of disclosure of private information and intrusion upon seclusion to determine if the harm she alleges is “the kind of harm caused by the comparator tort[s].”   The Third Circuit found that she failed to identify sufficiently concrete harms under either analogy.

  1. Tracking Information That Is Not Personal Or Sensitive Nor Disclosed Publicly Not Sufficient To Allege Concrete Injury

With regard to the disclosure of private information analogy, the Third Circuit found that the information captured by the session replay code — recording clicks, mouse hovers, and search bar searches — was neither sensitive or personal.  In support of this conclusion, the Third Circuit reasoned that the disclosure of such information cannot plausibly be said to result in embarrassment or humiliation.  Cook did not share her name, contact information, address, or billing information while on GameStop’s website.  Further, though Cook alleged that GameStop obtained information about her device and browser and created a unique ID and profile for her to capture the session replay information, she did not allege that GameStop identified her through this information.  Id. at 160.  Cook alleged only that if a user “eventually identifies themselves” then GameStop could “back-reference all of that user’s other web browsing.”   Id.  The Third Circuit found these allegations were too hypothetical to meet Article III’s injury-in-fact requirement.

Going one step further, the Third Circuit found that “even assuming the information was the type that could cause Cook humiliation under ‘public scrutiny,’” Cook did not allege that the information was ever publicized or disclosed publicly.  Id.  Cook alleged only that the information was disclosed to third-party vendor Microsoft, “not the broader public.”  Id. 

As the information collected was not personal or sensitive, the Third Circuit also rejected Cook’s intrusion upon seclusion analogy.  As an additional basis for rejecting this tort analogy, the Third Circuit acknowledged that “[m]ost of us understand that what we do on the Internet is not completely private.”   Id. (citation omitted). 

  1. The WESCA Does Not Provide A Statutory Avenue For Circumventing The Injury-In-Fact Requirement For Standing

The Third Circuit next considered and rejected Cook’s argument that the WESCA provides a separate avenue to circumvent Article III’s injury-in-fact requirement.  In making this argument, Cook relied on language in the TransUnion decision that the legislature can “‘elevate harms that exist in the real world’ to make them legally actionable” and went on to claim the WESCA did just that in protecting a “wider range of information” from collection during electronic communications.  The Third Circuit disagreed with this logic and reading of the TransUnion decision, determining that the theory “contradicts the fundamental holding of TransUnion” which instructs courts to consider the concrete harm actually alleged by the Plaintiff rather than the “harm the statutory cause of action typically protects against.”   Id.at 161 (emphasis added).  The Third Circuit analyzed that a statutory violation of the WESCA for tracking web browsing information does not dispense with the Article III standing inquiry and Cook was still required to articulate a harm existing in the “real world” under TransUnion, as legislatures cannot “transform something that is not remotely harmful into something that is.”  Id. 

  1. Precedent In Which Website Operators Affirmatively Represented They Would Not Track Information Are Not Controlling

The Third Circuit further opined that the Nickelodeon and Google II decisions — which Cook cited in favor of her argument that tracking internet browsing history has been found to constitute a concrete harm — were not controlling.  The Third Circuit explained that Nickelodean involved claims that a website operator was collecting minors’ personal information despite affirmatively representing that it would not do so.  Id. at 162 (citing In Re Nickelodeon Consumer Priv. Litig., 827 F.3d 262, 269 (3d Cir. 2016)).  And, similarly, Google II involved allegations that Google bypassed browser privacy settings through the use of browser cookies to track user information.  Id. (citing In Re Google Inc. Cookie Placement Consumer Priv. Litig., 934 F.3d 316, 321 (3d Cir. 2019) (Google II)).  The Third Circuit found that both were instances of affirmative “promises not to” collect information that the website operator collected in any event.  Id.  Here, by contrast, Cook failed to identify an affirmative representation on the part of GameStop to refrain from tracking user browsing and website usage information.

  1. Current Status of GameStop Action

A mandate was issued on September 12, 2025 transferring the action back to the jurisdiction of the District Court, where the matter is still pending.

Implications for Website Operators Tracking Browsing History and Use:

The Third Circuit has provided a helpful roadmap for website operators — at least in this jurisdiction — that merely tracking clicks and interaction with a website is insufficient to confer standing in federal court to potential plaintiffs challenging such tracking.  It is critical that the tracking at issue in GameStop, however, did not collect personal or sensitive information nor disclose the same.  GameStop also did not affirmatively represent that it would not track website use and interaction.  Website operators would be well-advised to review any website tracking using this rubric and to seek legal advice in the event of doubt or ambiguity. 

© 2009- Duane Morris LLP. Duane Morris is a registered service mark of Duane Morris LLP.

The opinions expressed on this blog are those of the author and are not to be construed as legal advice.

Proudly powered by WordPress