Crypto Class Action Key Decisions and Trends in 2025

By Justin Donoho

Duane Morris Takeaway: Available now is the recent article in the Legal Intelligencer by Justin Donoho entitled “Crypto Class Action Key Decisions and Trends in 2025.”  The article is available here and is a must-read for corporate counsel involved with crypto and blockchain technologies.

This year has already been a busy one in the crypto class action litigation landscape.  It has seen several significant court decisions that have continued to shape the law in this growing area, including decisions on dispositive motions regarding whether various crypto transactions are sales of unregistered “securities” and, if so, whether the operator of a crypto exchange may be held liable for such transactions.  Two class certification split decisions were also issued, showing why claims for the sale of unregistered securities remain popular with the plaintiffs’ bar whereas other types of claims increasingly being brought the plaintiff’s bar face significant hurdles to class certification.  There have also been several multimillion-dollar crypto class action settlements.  In addition, dozens of new crypto class action cases have been filed, auguring a continued trend of further development in this area.  This article analyzes these key decisions and trends.

Implications For Corporations

With crypto assets continuing to proliferate and the current presidential administration reducing enforcement priorities relating to sales of crypto assets, crypto class action litigation is multiplying.  We should expect to see an upward trend of key decisions and new cases in the remainder of this year and beyond, as this burgeoning area of the law continues to unfold.

New York Federal Court Dismisses Adtech Class Action Because No Ordinary Person Could Identify Web User

By Gerald L. Maatman, Jr., Justin Donoho, Hayley Ryan, and Ryan Garippo

Duane Morris Takeaways:  On September 3, 2025, in Golden v. NBCUniversal Media, LLC, No. 22-CV-9858, 2025 WL 2530689 (S.D.N.Y. Sept. 3, 2025), Judge Paul A. Engelmayer of the U.S. District Court for the Southern District of New York granted a motion to dismiss with prejudice for a media company on a claim that the company’s use of website advertising technology on its website violated the Video Privacy Protection Act (“VPPA”).  The ruling is significant as it shows that in the explosion of adtech class actions across the nation seeking millions or billions of dollars in statutory damages under not only the VPPA but also myriad other statutes providing for statutory penalties on similar theories that the website owner disclosed website activities to Facebook, Google, and other advertising agencies, the statute and its harsh penalties should not be triggered because no ordinary person could access and decipher the information transmitted.

Background

This case is one of a multiplying legion of class actions that plaintiffs have filed nationwide alleging that Meta Pixel, Google Analytics, and other similar software embedded in defendants’ websites secretly captured plaintiffs’ web-browsing activity and sent it to Meta, Google, and other online advertising agencies.

This software, often called website advertising technology or “adtech,” is a common feature on corporate, governmental, and other websites in operation today.  In adtech class actions, the key issue is often a claim brought under the VPPA, a federal or state wiretap act, a consumer fraud act, and even the Illinois Genetic Information Privacy Act (GIPA), because plaintiffs often seek millions (and sometimes even billions) of dollars, even from midsize companies, on the theory that hundreds of thousands of website visitors, times $2,500 per claimant in statutory damages under the VPPA, for example, equals a huge amount of damages.  Plaintiffs have filed the bulk of these types of lawsuits to date against healthcare providers, but they also have filed suits against companies that span nearly every industry including retailers, consumer products, and universities.  Several of these cases have resulted in multimillion-dollar settlements, several have been dismissed, the vast majority remain undecided, and especially with some district courts being more permissive than others in allowing adtech class actions to proceed beyond the motion to dismiss stage (as we blogged about here), the plaintiffs’ bar continues to file adtech class actions at an alarming rate.

In Golden, the plaintiff brought suit against a media company.  According to the plaintiff, she signed up for an online newsletter offered by the media company and, thereafter, visited the media company’s website, where she watched videos.  Id. at *2-4.  The plaintiff further alleged that, after she watched those videos, her video-watching history was sent to Meta without her permission via the media company’s undisclosed use of the Meta Pixel on its website.  Id.  Like plaintiffs in most adtech class action complaints, this plaintiff: (1) alleged that before the company sent the web-browsing data to the online advertising agency (e.g., Meta), the company encrypted the data via the secure “https” protocol (id., ECF No. 56 ¶ 45); and (2) did not allege that any human had her encrypted web-browsing data or could retrieve it from the advertising agency’s algorithms or that even the advertising agency, or any other entity or person, has her web-browsing data stored or could retrieve it from the advertising agency’s algorithms in a decrypted (readable) format.  Based on the plaintiffs’ allegations, the plaintiff alleged a violation of the VPPA.

The media company moved to dismiss under Rule 12(b)(6), arguing that the media company did not adequately allege that the media company “disclosed” the plaintiff’s “personally identifiable information” (“PII”), defined under the VPPA as “information which identifies a person as having requested or obtained specific video materials or services….”  Id., 2025 WL 2530689, at *5-6.

The Court’s Decision

The Court agreed with the media company and held that the plaintiff failed plausibly to plead any unauthorized “disclosure.” 

As the Court explained, “PII, under the VPPA, has three distinct elements: (1) the consumer’s identity, (2) the video material’s identity, and (3) the connection between them.”  Id. at *6.  Moreover, PII “encompasses information that would allow an ordinary person to identify a consumer’s video-watching habits, but not information that only a sophisticated technology company could use to do so.”  Id. (emphasis in original).  Therefore, “to survive a motion to dismiss, a complaint must plausibly allege that the defendant’s disclosure of information would, with little or no extra effort, permit an ordinary recipient to identify the plaintiff’s video-watching habits.”  Id.  For these reasons, explained the Court, the Second Circuit has “effectively shut the door for Pixel-based VPPA claims.”  Id. at *7 (citing Hughes v. National Football League, 2025 WL 1720295 (2d Cir. June 20, 2025)).

Applying these standards, the Court dismissed the plaintiff’s VPPA claim with prejudice, holding that, “[i]n short, because the alleged disclosure could not be appreciated — decoded to reveal the actual identity of the user, and his or her video selections — by an ordinary person but only by a technology company such as Facebook, it did not amount to PII.”  Id. at *6-7.  In so holding, the Court cited an “emergent line of authority” shutting the door on VPPA claims not only in the Second Circuit but also in other U.S. Courts of Appeal.  See In Re Nickelodeon Consumer Priv. Litig., 827 F.3d 262, 283 (3d Cir. 2016) (affirming dismissal of VPPA case involving the use of Google Analytics, stating, “To an average person, an IP address or a digital code in a cookie file would likely be of little help in trying to identify an actual person”); Eichenberger v. ESPN, Inc., 876 F.3d 979, 986 (9th Cir. 2017) (affirming dismissal of VPPA case because “an ordinary person could not use the information that Defendant allegedly disclosed [a device serial number] to identify an individual”).

Implications For Companies

The Court’s holding in Golden is a win for adtech class action defendants and should be instructive for courts around the country addressing adtech class actions brought under not only the VPPA, but also other statutes prohibiting “disclosures,” and the like.  These statutes should be interpreted similarly to require proof that an ordinary person could access and decipher the web-browsing data, identify the person, and link the person to the data. 

Consider a few examples.  A GIPA claim requires proof of a disclosure or a breach of confidentiality and privilege.  An eavesdropping claim under the California Information of Privacy Act (CIPA) § 632 requires proof of eavesdropping.  A trap and trace claim under CIPA § 638.51 requires proof that the data captured is reasonably likely to identify the source of the data.  A claim under the Electronic Communications Privacy Act (ECPA) requires proof of an interception.

When adtech sends encrypted, inaccessible, anonymized transmissions to the advertising agency’s algorithms, has there been any disclosure or breach of confidentiality and privilege (GIPA), eavesdropping (CIPA § 632), data capture reasonably likely to identify the source (CIPA § 638.51), or interception (ECPA)?  Just as adtech transmissions are insufficient to amount to a disclosure under the VPPA, Golden shows neither should adtech transmissions trigger these similarly worded statutes because no ordinary person could access and decipher the data transmitted.
Best Practices To Mitigate The Risk Of Class Action Litigation Over AI Pricing Tool Noncompliance With Antitrust And AI Statutes

By Justin Donoho

Duane Morris Takeaway: Available now is the recent article in the Journal of Robotics, Artificial Intelligence & Law by Justin Donoho entitled “Ten Design Guidelines to Mitigate the Risk of AI Pricing Tool Noncompliance with the Federal Trade Commission Act, Sherman Act, and Colorado AI Act.”  The article is available here and is a must-read for corporate counsel involved with development or deployment of AI pricing tools.

While artificial intelligence (AI) pricing tools can improve revenues for retailers, suppliers, hotel operators, landlords, ride-hailing platforms, airlines, ticket distributors, and more, designers and deployers of such tools increasingly face the risk of being targeted in lawsuits brought by governmental bodies and class action plaintiffs alleging unfair methods of competition in violation of the Federal Trade Commission (FTC) Act and agreements that restrain trade in violation of the federal Sherman Act.  This article identifies recently emerging trends in such lawsuits, including one currently on appeal in the U.S. Court of Appeals for the Third Circuit and three pending in district courts, draws common threads, and discusses ten guidelines that AI pricing tool designers should consider to mitigate the risk of noncompliance with the FTC Act, the Sherman Act, and Colorado AI Act.

Implications For Corporations

AI pricing tools designed to comply with antitrust and AI laws face fewer risks than those not designed for compliance, of an expensive class action lawsuit or government-initiated proceeding alleging violation of such laws.  Moreover, by enabling and automating informed pricing decisions, AI pricing tools hold the potential to drive market efficiencies.  This article identifies best practices to assist with such compliance and, relatedly, such market efficiencies.

Illinois Federal Courts Allow Adtech And Edtech ECPA Claims To Proceed, Furthering Split Of Authority

By Gerald L. Maatman, Jr., Justin Donoho, Hayley Ryan, and Tyler Zmick

Duane Morris Takeaways:  On August 20, 2025, in Hannant v. Sarah D. Culbertson Memorial Hospital, 2025 WL 2413894 (C.D. Ill. Aug. 20, 2025), Judge Sara Darrow of the U.S. District Court for the Central District of Illinois granted a motion to dismiss while allowing a website user to re-plead her claim that the hospital’s use of website advertising technology (“adtech”) violated the Electronic Communications Privacy Act (“ECPA”).  The same day, in Q.J. v. Powerschool Holdings, LLC, 2025 WL 2410472 (N.D. Ill. Aug. 20, 2025), Judge Jorge Alonso of the U.S. District Court for the Northern District of Illinois denied the Chicago school board and its educational technology (“edtech”) provider’s motion to dismiss a claim that their use of a third-party data analytics tool violated the ECPA.  These rulings are significant in that they show that in the hundreds of adtech, edtech, and other internet-based technology class actions across the nation seeking millions (or billions) in dollars in statutory damages under the ECPA, Illinois Federal courts have distinguished themselves from other courts in other jurisdictions that have refused to interpret the ECPA in such a plaintiff-friendly manner as have the Illinois Federal courts. 

Background

These cases are two of a legion of class actions that plaintiffs have filed nationwide alleging that Meta Pixel, Google Analytics, and other similar software embedded in defendants’ websites secretly captured plaintiffs’ web-browsing data and sent it to Meta, Google, and other online advertising agencies and/or data analytics companies.  In these adtech, edtech, and similar class actions, the key issue is often a claim brought under the ECPA on the theory that hundreds of thousands of website visitors times $10,000 per claimant in statutory damages equals a huge amount of damages.  Plaintiffs have filed the bulk of these types of lawsuits to date against healthcare providers, but they have filed suits against companies that span nearly every industry including education, retailers, and consumer products.  Several of these cases have resulted in multimillion-dollar settlements, several have been dismissed, and the vast majority remain undecided.

In Hannant, the plaintiff brought suit against a hospital.  According to the plaintiff, the hospital installed the Meta Pixel on its website, thereby transmitting to Meta, allegedly without the plaintiff’s consent, data about her visit to the hospital’s website. 

In Q.J., the plaintiff brought suit against the Chicago school board and its edtech provider.  According to the plaintiff, the school board and edtech provider installed a third-party data analytics tools called Heap Autocapture on the edtech provider’s online platform, thereby transmitting to Heap, allegedly without consent, information about the students’ visits to the online platform.

In both lawsuits, the plaintiffs claimed that these alleged events amounted to an “interception” by the defendant that violated the ECPA.  Neither defendant contested whether the plaintiff had plausibly alleged an “interception,” even though the events were more like the catching and forwarding of a different ball, not an interception: (1) as alleged in Hannant, see No. 24-CV-4164, ECF No. 14 ¶¶ 49, 363 (alleging that the communication Meta received was not the same transmission but a “duplicate[]” that was “forward[ed]”); and (2) despite the wholly conclusory allegations of a purported “interception” in Q.J.  However, both defendants moved to dismiss the claim under the ECPA on the grounds that, to the extent there was any interception, no liability exists under the ECPA pursuant to its exception where the party does not act “for the purpose of committing any criminal or tortious act.” 18 U.S.C. 2511(2)(d).

The Courts’ Decisions

In Hannant, the Court dismissed the ECPA claim without prejudice, and granted the plaintiff leave to re-plead in a fashion that may allow such an amended complaint to withstand the ECPA claim.  Specifically, the Court found that an amendment might plausibly allege a criminal or tortious purpose by adding sufficient detail about the plaintiff’s website interactions to show that there had been a violation of the Health Insurance Portability and Accountability Act (“HIPAA”), which provides for criminal and civil penalties against a person “who knowingly … discloses individually identifiable health information [(‘IIHI’)] to another person.”  2025 WL 2413894,at *3 (quoting 42 U.S.C. § 1320d-6).  As the Court explained, under adtech class-action precedent in the U.S. District Court for the Northern District of Illinois, adding additional detail regarding alleged transmission of IIHI could be enough to allege a criminal or tortious purpose.  Id. at *3-5.

In Q.C., the Court denied the school board and edtech provider’s motion to dismiss, citing the same plaintiff-friendly precedent in the Northern District of Illinois cited by the opinion in Hannant, and explaining that while the allegedly disclosed data in this educational context did not violate the HIPAA, the plaintiff had plausibly alleged that the transmissions at issue violated the Illinois School Student Records Act (“ISSRA”), 105 ILCS 10/6, and Family Educational Rights and Privacy Act (“FERPA”), 20 U.S.C. § 1232g.  2025 WL 2410472, at *6.

Implications For Companies

In Illinois Federal courts, pixels and cookies are no longer just marketing and educational tools – they are legal risk vectors.  By contrast, other U.S. District Courts ruling on Rule 12(b)(6) motions have found no plausibly alleged interception when an internet-based communication is forwarded as opposed to being intercepted mid-flight, and no plausibly alleged criminal or tortious purpose because the purpose was not to violate any statute but rather to engage in advertising or data analytics.  (See, e.g., our prior blog entry discussing one of these several cases, here.)Website owners facing lawsuits in Illinois District Courts would do well to press such arguments finding success in other jurisdictions in order to preserve them for appeal in the Seventh Circuit, which has yet to rule on these issues.  In addition, other defenses remain, including demonstrating that plaintiffs cannot meet their burden of proof to show any actual disclosure where transmissions of information entered on the website to adtech vendors and data analytics providers such as Meta or Google are encrypted, ephemeral, anonymized, aggregated, and otherwise unviewable and irretrievable by any human and hence not any actual disclosure to a third party.

Corporate counsel seeking to deter ECPA litigation should keep in mind the following best practices (discussed in more detail in our prior blog post, here): (1) add or update arbitration clauses to deter class actions and mitigate the risks of mass arbitration; (2) update website terms of use, data privacy policies, and vendor agreements; and (3) audit and adjust uses of website advertising technologies.

Ninth Circuit Affirms Summary Judgment For Defendant On CIPA Claim For Aiding And Abetting Third-Party Software Provider

By Gerald L. Maatman, Jr., Justin Donoho, and Ryan Garippo

Duane Morris Takeaways:  On July 9, 2025, in Gutierrez, et al. v. Converse, Inc., No. 24-4797, 2025 WL 1895315 (9th Cir. July 9, 2025), the Ninth Circuit affirmed that a plaintiff had no evidence from which a reasonable jury could conclude that an online retailer’s use of third-party software to enable a chat feature on its website aided and abetted the third-party vendor in reading or attempting to read the contents of the plaintiff’s chat messages real-time in alleged violation of the California Invasion of Privacy Act (CIPA).  In rejecting this theory, the ruling is significant because it shows that CIPA claims involving alleged disclosures of website activities to third-party software providers cannot survive unless the plaintiff can show that the website owner enabled the third party to read unencrypted, real-time communications. 

Background

This case is one of a legion of class actions that plaintiffs have filed nationwide alleging that third-party software embedded in defendants’ websites secretly captured plaintiffs’ web-browsing activity and sent it to the third-party provider of the software.  Third-party software is a common feature on many websites today and comes in many forms including website advertising technologies (“adtech”), customer relationship management (“CRM”) software, enterprise resource management (“ERP”) software, and, as in this case, communications platforms.

In Gutierrez, Plaintiff brought suit against an online retailer.  According to Plaintiff, the retailer installed a chat feature on its public-facing website and thereby transmitted chat communications entered on the website to Salesforce, a third-party provider of the chat feature to the online retailer in the form of “software as a service” (“SaaS”).  2024 WL 3511648, at *2 (C.D. Cal. July 12, 2024). 

As usual since the Snowden disclosures in 2013, all of these transmissions between the web user, website, and third-party software provider were “were encrypted while in transit.”  Id. at *3.  Moreover, as is true for all internet communications, the chats were transmitted “in different network packets.”  Id.  Thus, the uncontroverted expert evidence showed that “it is ‘virtually impossible’ to learn the contents of an internet communication while it is in transit.”  Id.

The online retailer’s chat data, including chat transcripts, were stored on Salesforce’s servers.  Id.  However, this information was accessible in unencrypted format only through the retailer’s password-protected dashboard.  Id.  Plaintiff offered no evidence to show that Salesforce had access to the retailer’s dashboard or that the retailer ever provided Salesforce access to it.  Id.

Based on these facts, Plaintiff argued that the retailer violated the CIPA by aiding and abetting Salesforce’s wiretapping or attempts to learn her chat communications on the retailer’s website. 

The District Court granted the retailer’s motion for summary judgment for multiple reasons.  First, the District Court found as a matter of law that Salesforce did not violate CIPA’s first clause prohibiting intentional wiretapping or making any unauthorized connection “with any telegraph or telephone wire, line, cable, or instrument” because “Courts have consistently interpreted this clause as applying only to communications over telephones and not through the internet.”  Id. at *6-7. 

Second, the District Court found no genuine dispute of material fact existed as to whether Salesforce had violated the second clause of CIPA, Section 631(a), “because Plaintiff has presented no evidence from which a reasonable jury could conclude Salesforce intercepts messages sent through [the retailer]’s chat feature ‘while … in transit’ or reads or attempts to read or learn the contents of such messages.”  Id. at *7.  As the District Court explained, “uncontroverted evidence establishes messages sent through [the retailer]’s chat feature are encrypted while in transit and, moreover, it is ‘virtually impossible’ to learn the contents of an internet communication while it is in transit because internet communications are transmitted ‘in different network packets[.]’”  Further, the District Court stated that “the fact that a user is redirected to a Salesforce-owned URL upon opening the chat feature on [the retailer]’s website does not establish the user’s messages are sent to Salesforce or Salesforce reads or attempts to read or learn the contents of such messages. Rather, this fact simply establishes . . . the user’s messages are transmitted to [the retailer]’s Service Cloud application.”  Id.  In addition, the District Court explained that “the existence of UUID [Universally Unique Identifier] values attached to chat messages and the mere possibility Salesforce ‘can’ use these values to ‘connect the dots’ between data are insufficient to establish a genuine issue of material fact as to whether Salesforce reads or attempts to read users’ messages while they are in transit.”  Id.

Finally, the District Court found that “because Plaintiff has not established an underlying violation of Section 631(a)’s first or second clause by Salesforce, [the retailer] cannot be liable for aiding and abetting Salesforce.”

The Ninth Circuit’s Opinion

The Ninth Circuit agreed with the retailer. It found that summary judgment for the retailer was warranted and affirmed the order below. 

In a short opinion, the Ninth Circuit affirmed the District Court’s opinion by finding that “no evidence exists from which a reasonable jury could conclude” that Salesforce engaged in wiretapping or attempted to learn Plaintiff’s chat communications on the retailer’s website and, therefore, absent an underlying violation by Salesforce, no aiding and abetting liability by the retailer.  Id., at *1.

Circuit Judge Jay Bybee agreed, filing a separate concurring opinion stating that the wiretapping claim should be affirmed because “the statute, as passed in 1967, focuses on the wiretapping of telegraph or telephone wires—it criminalizes, as relevant here, the wiretapping of a telephone call” and, thus, CIPA’s clause prohibiting wiretapping “does not apply to the internet.”  Id. at *2-3.  Further, Judge Bybee opined: “Until and unless the California appellate courts tell us otherwise, or the California legislature amends § 631(a), I refuse to apply § 631(a)’s first clause to the internet.”  Id. at *3. 

Implications For Companies

The District Court’s holding and Ninth Circuit’s affirmance in Gutierrez are a win for CIPA class action defendants and should be instructive for courts around the country.  In the hundreds of CIPA class actions alleging a defendant’s disclosure of web-browsing activities to an adtech provider, for example, the plaintiff typically does not allege that the adtech provider has any ability to read any unencrypted version of the information disclosed.  This is not surprising, since the largest adtech providers often alleged in CIPA adtech class actions typically encrypt, anonymize, aggregate, and otherwise prevent their own ability to access web users’ browsing activities in any unencrypted format. 

Gutierrez shows that adtech plaintiffs will need to show, however, that the owner of the website they visited enabled the third party adtech provider to read unencrypted, real-time communications, in order to prove their CIPA claims.

Data Security and Privacy Liability – Takeaways From The Sedona Conference Working Group 11 Annual Meeting in Redmond, WA

By Justin R. Donoho

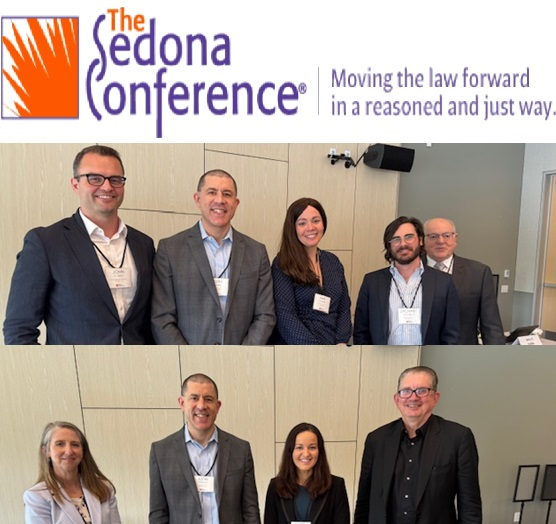
Duane Morris Takeaways: Data privacy and data breach class action litigation continue to explode.  At the Sedona Conference Working Group 11 on Data Security and Privacy Liability, at Microsoft’s campus in Redmond, Washington, on May 7, 2025, Justin Donoho of the Duane Morris Class Action Defense Group served as a dialogue leader for two panel discussions, “Individual Liability for Data Security Failures” and “Privacy and Data Security Litigation Update.”  The working group meeting, which spanned two days and had over 50 participants, produced excellent dialogues on these topics and others including AI statutory guidance, shifting U.S. federal regulatory priorities in the privacy and data security landscape, privacy and data security state regulator roundtable, emerging issues and trends in the cyber threat landscape, and law firm data security.

The Conference’s robust agenda featured over 30 dialogue leaders from a wide array of backgrounds, including government officials, data security industry experts, a district court judge, in-house attorneys, cyber and data privacy law professors, plaintiffs’ attorneys, and defense attorneys.  In a masterful way, the agenda provided valuable insights for participants toward this working group’s mission, which is to identify and comment on trends in data security and privacy law, in an effort to help organizations prepare for and respond to data breaches, and to assist attorneys and judicial officers in resolving questions of legal liability and damages.

Justin had the privilege of speaking about current trends in cases seeking individual liability for data security failures and in data privacy class actions.  A few of the highlights from his presentations included discussing the SEC’s case brought against SolarWinds’ CISO Michael Brown, which has CISOs worldwide on the edges of their seats (discussed in Justin’s article here), and two recent cases resulting in helpful precedent for defendants facing cases alleging privacy violations for their uses of website advertising technologies (adtech), including a case that disposed of an adtech class action due to consent by browsewrap (see here), and a case that dismissed an adtech class action due to ambiguities found in a wiretap statute (see here).

Finally, one of the greatest joys of participating in Sedona Conference meetings is the opportunity to draw on the wisdom of fellow presenters and other participants from around the globe.  Highlights included:

  1. A lively dialogue among some of my panelists and other participants regarding trends in decisions regarding Article III standing and the costs and benefits defendants should consider when deciding whether to seek dismissal due to plaintiffs’ lack of Article III standing.
  2. State regulators giving candid advice regarding what and what not to do following data breaches in terms of notifying their offices, participating in investigations, and attempting to negotiate settlements. 
  3. Experts of all stripes dissecting the Colorado Privacy Act, Colorado AI Act, and those statutes’ application to AI hiring tools in an effort to offer guidance to future legislators drafting similar statutes.
  4. Seasoned defense attorneys discussing how federal agencies responsible for rules regarding privacy and data security have responded to the new presidential administration’s “Regulatory Freeze Pending Review” memorandum, the personnel changes, actions, and reviews taken during the first months of the new administration, and the implications for regulated organizations.
  5. Cyber and cyber insurance experts leading a dialogue about emerging risks, regulatory challenges, liability concerns, and underwriting processes relating to cybersecurity.
  6. Law firm consultants addressing current issues with AI that law firms should consider when crafting their cybersecurity assessments, policies, and procedures.

Thank you to the Sedona Conference Working Group 11 and its incredible team, the fellow dialogue leaders, the engaging participants, and all others who helped make this meeting in Redmond, Washington, an informative and unforgettable experience.

For more information on the Duane Morris Class Action Group, including its Data Privacy Class Action Review e-book, and Data Breach Class Action Review e-book, please click the links here and here.

Best Practices To Mitigate The Risk Of AI Hiring Tool Noncompliance With Antidiscrimination Statutes

By Justin Donoho

Duane Morris Takeaway: Available now is the recent article in the Journal of Robotics, Artificial Intelligence & Law by Justin Donoho entitled “Five Human Best Practices to Mitigate the Risk of AI Hiring Tool Noncompliance with Antidiscrimination Statutes.”  The article is available here and is a must-read for corporate counsel involved with development or deployment of AI hiring tools.

While artificial intelligence (AI) hiring tools can improve efficiencies in human resource functions, such as candidate sourcing, resume screening, interviewing, and background checks, AI has not replaced the need for humans to ensure that AI-assisted human resources (HR) practices comply with a wide range of antidiscrimination laws such as Title VII of the Civil Rights Act of 1964 (Title VII), the Americans with Disabilities Act (ADA), the Age Discrimination in Employment Act (ADEA), the sections of Colorado’s AI Act setting forth developers’ and deployers’ “duty to avoid algorithmic discrimination” (CAI), New York City’s law regarding the use of automated employment decision tools (NYC’s AI Law), the Illinois AI Video Act (IAIVA), and the 2024 amendment to the Illinois Human Rights Act to regulate the use of AI (IHRA).  This article identifies human best practices to mitigate the risk of companies’ AI hiring tools violating the foregoing statutes, according to the statutes, EEOC regulations, and scholarly sources authored by EEOC personnel and leading data scientists.

Implications For Corporations

AI hiring tools designed to comply with antidiscrimination statutes will comply.  Moreover, by eliminating some human decision-making and replacing it with carefully designed algorithms, AI holds the potential to substantially reduce the kind of bias that has been unlawful in the United States since the civil rights movement of the mid-twentieth century.  This article identifies human best practices to assist with such compliance and, relatedly, such potential substantial reduction of bias.

Pennsylvania Federal Court Disposes Of Adtech Class Action Due To Consent By Browsewrap

By Justin Donoho and Gerald L. Maatman, Jr.

Duane Morris Takeaways:  On March 24, 2025, in  Popa v. Harriet Carter Gifts, Inc., 2025 WL 896938 (W.D. Pa. Mar. 24, 2025), Judge William S. Stickman IV of the U.S. District Court for the Western District of Pennsylvania granted summary judgment for a retailer on a claim that the retailer’s use of website advertising technology violated the Pennsylvania Wiretapping and Electronic Surveillance Control Act (“WESCA”).  The ruling is significant as it shows that in the hundreds of adtech class actions across the nation seeking millions or billions of dollars in statutory damages under various federal and state wiretap acts, implied consent may be found as a matter of law, thus disposing of the wiretap claim, where the defendant has posted a clearly labeled privacy statement at the bottom of the relevant webpage that discloses the use of adtech.

Background

This case is one of a legion of class actions that plaintiffs have filed nationwide alleging that Meta Pixel, Google Analytics, and other similar software embedded in defendants’ websites secretly captured plaintiffs’ web browsing data and sent it to Meta, Google, and other online advertising agencies. 

This software, often called website advertising technologies or “adtech,” is a common feature on millions of corporate, governmental, and other websites in operation today.  In adtech class actions, the key issue is often a claim brought under a federal or state wiretap act, a consumer fraud act, or the Video Privacy Protection Act, because plaintiffs often seek millions (and sometimes even billions) of dollars, even from midsize companies, on the theory that hundreds of thousands of website visitors, times $10,000 per claimant in statutory damages under the Federal Wiretap Act, for example, equals a huge amount of damages.  Plaintiffs have filed the bulk of these types of lawsuits to date against healthcare providers, but they have filed suits against companies that span nearly every industry including retailers, consumer products, and universities.  Several of these cases have resulted in multimillion-dollar settlements, several have been dismissed, and the vast majority remain undecided. 

In Popa, the plaintiff brought suit against a retailer.  According to the plaintiff, the retailer installed adtech called NaviStone OneTag on its public-facing website, thereby transmitting to Navistone, allegedly without the plaintiff’s consent, data about her visit to the retailer’s website where she added a set of pet stairs to her shopping cart.   See id., 52 F.4th 121, 124-25 (3d Cir. 2022) (referenced in id., 2025 WL 896938).  Based on these allegations, the plaintiff claimed that the retailer aided Navistone to intercept her communications in violation of the WESCA.  Id., 2025 WL 896938, at *1. 

The retailer moved for summary judgment, arguing that the plaintiff consented because of the nature of the internet or, alternatively, due to the retailer’s “Privacy Statement” linked at the bottom of the retailer’s webpage in a color contrasting with the website’s background, as is common on many websites, and which disclosed the retailer’s use of adtech.  Id. at *2.

The Court’s Decision

The Court agreed with the retailer and held that the plaintiff impliedly consented to the retailer’s privacy policy, thereby defeating the plaintiffs’ WESCA claim.

Central to the Court’s holding was the WESCA’s statutory exception rendering it inapplicable “where all parties to the communication have given prior consent to such interception.”  Id. at *5 (quoting 18 Pa. C.S. § 5704(4)).   As the Court explained, “actual knowledge is not required under the mutual consent provisions of WESCA” and “‘prior consent’ can be demonstrated when the person being recorded knew or should have known, that the conversation was being recorded. This standard is one of a reasonable person, and not proof of the subjective knowledge of the person being recorded.”  Id. at **5-6.  In short, the Court reasoned that “the WESCA mutual consent exception focuses on a reasonable person standard.”  Id. at *6.

To determine the reasonable person standard under the WESCA, the Court rejected the retailer’s first argument that any reasonable person using the internet impliedly consents to the use of adtech because of the nature of the internet.  As the Court found, “the nature of the internet does not confer blanket implied consent to interception under WESCA.”  Id. at *7.  However, as the Court further found that “a reasonably prudent person has a lower expectation of privacy on the internet than on, for example, a telephone, which lacks the entire system of trackers, cookies, and algorithms commonly, if not ubiquitously, implicated in the use of a website.”  Id. at *7.

Having found that WESCA’s reasonable person standard involves a lower expectation of privacy on the internet than on the telephone, the Court applied this standard to the relevant facts of the case.  In doing so, the Court found that although the plaintiff did not actually read the Privacy Statement and therefore did not actually consent, if she were a reasonable person using the internet as the Court deemed her to be, then she had constructive knowledge as a matter of law due to a “browsewrap” agreement and therefore impliedly consented.  As the Court explained, “Contracts formed on the Internet [include] ‘browsewrap’ agreements, where a website’s terms and conditions of use are generally posted on the website via a hyperlink at the bottom of the screen.  Unlike a clickwrap agreement, a browsewrap agreement does not require the user to manifest assent to the terms and conditions expressly a party instead gives his assent simply by using the website.”  Id. at *9.

In conclusion, the Court found a browsewrap agreement as a matter of law and ordered entry of a judgment in the retailer’s favor based on the following facts: (1) the privacy statement “was specifically labeled ‘Privacy Statement.’ [The plaintiff], or any other user could have easily seen the link and understood exactly what it contained”; and (2) the retailer’s placement of a link to the privacy statement on the bottom of the relevant webpage was “in line with common usage”; and (3) “The hyperlink to the Privacy Statement was reasonably conspicuous. It was displayed in a white contrasting font against a blue background on the bottom of every page of the website.”  Id. at *11. 

In sum, the Court found that “these factors compel a finding that a reasonable person in [the plaintiff]’s position had constructive notice of the terms of the Privacy Statement as a matter of law.”  Id.

Implications For Companies

Popa provides powerful precedent for any company opposing adtech class action claims brought not only under the WESCA but also under any state or federal wiretap act, provided the company has a privacy policy sufficiently disclosing the use of adtech via a clearly labeled link on the bottom of the applicable webpage.  Consider, for example, the numerous adtech class actions featuring a claim under the Federal Wiretap Act and seeking millions or billions of dollars in statutory damages.  Although some courts have dismissed these claims on other grounds such as the lack of an interception or lack of criminal or tortious purpose (as discussed in our previous blog entry about a recent win for adtech defendants, here), other courts have refused to dismiss adtech claims brought under the Federal Wiretap Act, allowing them to proceed to costly merits, class certification, and expert discovery. 

Popa provides an alternative path to victory in these cases, where applicable, which is to show that the plaintiff implied consented to the adtech via browsewrap.

Federal Court Holds Illinois Genetic Privacy Claim Not Preempted By Federal Transportation Regulations

By Justin Donoho, Gerald L. Maatman, Jr., and Tyler Zmick

Duane Morris Takeaways:  In Short v. MV Transportation, Inc., No. 24-CV-3019 (N.D. Ill. Mar. 10, 2025), Judge Manish S. Shah of the U.S. District Court for the Northern District of Illinois denied defendant’s bid to dismiss a claim brought under the Illinois Genetic Information Privacy Act (“GIPA”).  In his ruling, Judge Shah acknowledged that U.S. Department of Transportation regulations require companies in the transportation industry (including defendant) to ensure their drivers satisfy certain physical qualification criteria.  The Court nonetheless rejected defendant’s argument that the regulations preempt the GIPA because they do not specifically require employers to ask applicants about their family medical histories (which the GIPA prohibits).  In other words, the Court denied defendant’s motion to dismiss because the GIPA does not make it “physically impossible” to comply with federal regulations. 

Background

Plaintiff Kevin Short alleged that he applied for a position as a driver for Defendant MV Transportation, Inc., a company that provides paratransit services.  As part of the application process, Plaintiff was required to complete a physical examination during which he was asked about his family medical history, including whether his family members had a history of high blood pressure, heart disease, or diabetes.

Plaintiff subsequently sued MV Transportation under the GIPA, alleging that the company violated Section 25(c)(1) of the statute by “solicit[ing], request[ing], [or] requir[ing] . . . genetic information of a person or a family member of the person . . . as a condition of employment [or] preemployment application.”  410 ILCS 513/25(c)(1).

MV Transportation moved to dismiss the complaint on the basis that the Department of Transportation’s (“DOT”) regulations preempted Plaintiff’s GIPA claim.  Specifically, MV Transportation argued that Plaintiff’s claim was barred under a “conflict preemption” theory because allowing the claim to proceed would force MV Transportation to choose between complying with the GIPA or complying with federal requirements to “conduct[ ] thorough physical examinations of its drivers.”

MV Transportation pointed to the Motor Carrier Safety Act for support, under which the DOT regulates commercial motor vehicle safety by promulgating “minimum safety standards” to ensure that “the physical condition of operators . . . is adequate to enable them to operate the vehicles safely” – including by requiring drivers to satisfy 13 “physical qualification criteria.”  49 U.S.C. § 31136(a)(3).

The Court’s Decision

In denying MV Transportation’s motion, the Court noted that conflict preemption applies only where “compliance with both federal and state regulations is a physical impossibility” or where the state law “stands as an obstacle to the accomplishment and execution of the full purposes and objectives of Congress.”  Id. at 6-7 (citations omitted); see also id. at 6 (noting that “‘[i]nvoking some brooding federal interest’ is insufficient to establish preemption; instead, MV Transportation must identify ‘a constitutional text or a federal statute’ that displaces or conflicts with the state law”) (quoting Virginia Uranium, Inc. v. Warren, 587 U.S. 761, 767 (2019)).  The Court further observed that MV Transportation had the burden of overcoming the “presumption against preemption.”

In its ruling, the Court concluded that it is not physically impossible for MV Transportation to simultaneously comply with the GIPA and DOT regulations relative to Plaintiff’s pre-employment health screening because the DOT regulations do not specifically require any inquiry into a driver’s family medical history.  MV Transportation asserted that DOT regulations nonetheless “contemplate[] that medical examiners may discuss” a person’s family medical history during a physical exam.  The Court was not persuaded, however, stating that such a scenario is “not enough to suggest that compliance with GIPA and the federal regulations is ‘physically impossible.’”  Id. at 9 (“The mere possibility that a medical examiner asks for information protected by GIPA while performing an examination does not demonstrate impossibility to comply with both federal and state law.”). 

The Court similarly held that the GIPA is not an obstacle to the execution of Congress’s purposes, as reflected in the Motor Carrier Safety Act and DOT regulations.  As support for this conclusion, the Court observed that the relevant DOL regulations and the GIPA serve different purposes – the regulations are meant to promote the safe operation of commercial motor vehicles, while the GIPA focuses on health information privacy. 

Implications Of The Decision

Short v. MV Transportation is one of several recent decisions in which courts denied bids to dismiss GIPA claims at the pleading stage. 

Given this litigation landscape and the statute’s strict penalty provision – under which statutory damages can quickly become significant ($2,500 per negligent violation and $15,000 per intentional or reckless violation, see 410 ILCS 513/40(a)(1)-(2)) – employers should ensure they comply with the statute regarding any health screenings they ask applicants or employees to complete (including by explicitly advising applicants and employees not to disclose their family medical histories during the screenings).

Data Privacy Class Action Alleges Insurers Improperly Collected The Data Of 40 Million Users Through Third-Party Applications

By Gerald L. Maatman, Jr., Justin Donoho, George J. Schaller, Ryan T. Garippo

Duane Morris Takeaways: In Mahoney, et al. v. The Allstate Corp, et al., 25-CV-01465 (N.D. Ill. Feb. 11, 2025), Plaintiffs Michael Mahoney and Scott Schultz (collectively, “Plaintiffs”) filed a putative class action lawsuit asserting Allstate, and its subsidiary Arity, illegally obtained personal driving data of 40 million policyholders through third-party mobile application software.  The case is pending in the U.S. District Court for the Northern District of Illinois before Judge Steven C. Seeger.This is the third lawsuit in a series of lawsuits alleging class-wide allegations based on Allstate’s alleged data collection practices.  See Sims et al. v. The Allstate Corp. et al., 1:25-CV-00407 (N.D. Ill. Jan. 14, 2025) (alleging data collection through third party application Sirius XM); see also Arellano et al. v. The Allstate Corp. et al., 1:25-CV-01256, (N.D. Ill. Feb. 5, 2025) (alleging data collection through third party applications Life360, GasBuddy, and Fuel Rewards). 

Mahoney, Sims, and Arellano, represent a triumvirate of data privacy class actions centered on allegations of improper data collection through third-party applications.  Companies will be well-served monitor these cases for their novel assertions in trending data privacy litigation.

Complaint Allegations

Michael Mahoney resides in San Francisco, California, and he downloaded the GasBuddy application in 2011 to “find competitive gas prices.”  Mahoney, 25-CV-01465, ECF No. 1 § III ¶ 14 (N.D. Ill. Feb. 11, 2025).  Scott Schultz resides in Highland Park, Illinois, and he downloaded the GasBuddy application in 2021 and used it “in his own and other people’s vehicles to find competitive gas prices.”  Id. § III ¶ 15.

Plaintiffs collectively allege that Allstate and its subsidiary Arity (collectively, “Defendants”) “conspired to collect drivers’ geolocation data and movement data from mobile devices, in-car devices, and vehicles.”  Id. § IV ¶ 7.  Plaintiffs allege Defendants designed a software development kit that could be integrated into third-party mobile applications such as “Routely, Life360, GasBuddy, and Fuel Rewards.”  Id.  § IV ¶ 8.  Plaintiffs further allege Defendant advertised that they “collect data ‘every 15 seconds or less’ from 40 million ‘active mobile connections’ and ‘derive[] unique insights that help insurers, developers, marketers, and communities understand and predict driving behavior at scale.”  Id. § IV ¶ 24.

Plaintiffs contend Defendants’ software development kit was “designed to and does collect data” including “Geolocation data and ‘GPS Points,’” “cellphone accelerometer, magnetometer, and gyroscopic data,” “Trip attributes” data (including start and end locations, trip distances, trip duration), “Derived events” data (including acceleration, speeding, distracted driving, crash detection), and “Metadata.”  Id. § IV ¶ 11 (A) – (E).  Plaintiffs further assert that when using these third-party applications “Defendants could collect real-time data on their locations and movements and surreptitiously collect highly sensitive and valuable data directly from Plaintiffs’ mobile phones.”  Id. § IV ¶ 16.

It is also important to note that Plaintiffs maintain that Defendants used their personal data to “develop, advertise, and sell several products and services to third parties, including insurance companies . . .” and used the purchased consumer data for “[Defendants’] own underwriting purposes.”  Id. § IV ¶ 23.  Plaintiffs, ultimately, assert that Defendants real purpose in using this data is for their “own financial and commercial benefit” and to obtain “substantial profit.”  Id. § V ¶ 49.  They ultimately assert via their nine-count Complaint that this technology amounts to a wiretapping of their personal information which entitles them, inter alia, to a sum of “$100 per day per violation or $10,000” per class member whichever is greater.  Id. § V ¶ 51.

Implications For Companies

Although such data collection lawsuits are no longer a new phenomenon, their scope has become far more aggressive as the plaintiffs’ bar continues to look for ways to monetize lawsuits against corporations using such technologies.

Take for example the dilemma presented by Mahoney.  In that case, it is likely that Defendants will have strong defenses to this action.  For example, Plaintiffs admit that Defendants’ purpose in using this technology was to earn “substantial profit.”  Id. § V ¶ 49.  Based on similar allegations, many courts have found that these purposes are insufficient for a plaintiff to avail itself of such wiretapping statutes.  See, e.g., Katz-Lacabe v. Oracle Am., Inc., 668 F. Supp. 3d 928, 945 (N.D. Cal. 2023) (dismissing wiretap claim because defendant’s “purpose has plainly not been to perpetuate torts on millions of Internet users, but to make money.”).

There are, however, enough court rulings that come out in the opposite direction to give a corporate defendant pause.  See, e.g., R.S. v. Prime Healthcare Services, Inc., No. 24-CV-00330, 2025 WL 103488, at *6-7 (C.D. Cal. Jan. 13, 2025) (recognizing the split and siding with the plaintiffs).  And, if Plaintiffs are correct that there are 40 million individuals in the class, and that each class member is entitled to $10,000 at a minimum, then this lawsuit alleges at least $400 billion dollars in liability.  Even if there is a 1% chance of success on these claims, it would suggest that the completely unrealistic figure of $4 billion dollars is on the table.

Corporations in these types of class actions are faced with the difficult choice of settling the claims for an astronomical figure based on the use of technologies which are ubiquitous in nature (like software development kits for mobile applications) or defend a $400 billion lawsuit based on defenses in an area of the law which is not fully developed.  It will be interesting to see how the Mahoney defendants balance these concerns as the case progresses, because many twists and turns lie ahead.

In the meantime, corporate counsel should take the opportunity to evaluate their companies’ data collection and privacy policies to make sure their companies are not easy targets.  If the allegations in Mahoney are any example, the mere threat of one of these lawsuits should be enough to keep corporate counsel up at night.  And, if their companies are ultimately sued in one of these lawsuits, they should ensure that an experienced defense team has its hands on the steering wheel. 

© 2009- Duane Morris LLP. Duane Morris is a registered service mark of Duane Morris LLP.

The opinions expressed on this blog are those of the author and are not to be construed as legal advice.

Proudly powered by WordPress